
Darren Death
-
Spaghetti and Marshmallows Game
Spaghetti & Marshmallows is a physics building game. You build towers, bridges and arms out of spaghetti and marshmallows, and the spaghetti bends and snaps the way the real thing does. It runs in a browser, as an installable web app and as an Android APK. Current version: 2.0.1. It has 61 levels in seven…
-
Verification Gaps Define the AI Production Era
Physical verification, credential attribution, and backup isolation now constrain AI-driven systems faster than model capability improves.
-
AI Agents, Zero Trust, and the New Insider Threat
Self-replicating prompt injections, unaudited AI agents, and eroding software controls reshape the security landscape.
-
Agent Safety, Cost, and Control at the Frontier
Misalignment findings, agent-driven skimming, and cheaper agent infrastructure reshape deployment decisions.
-
AI Inference Gaps and Ransomware Recovery Failures
DLP blind spots, runaway agents, identity-coupled backups, and audit’s measurement deficit.
-
Security Teams Build Their Own AI Agents as Vendor Tools Fall Short
Custom agents, browser-memory phishing, OWASP patch automation, and a Gartner warning on SOC AI evaluation gaps.
-
Daedelus Demo: Tetris
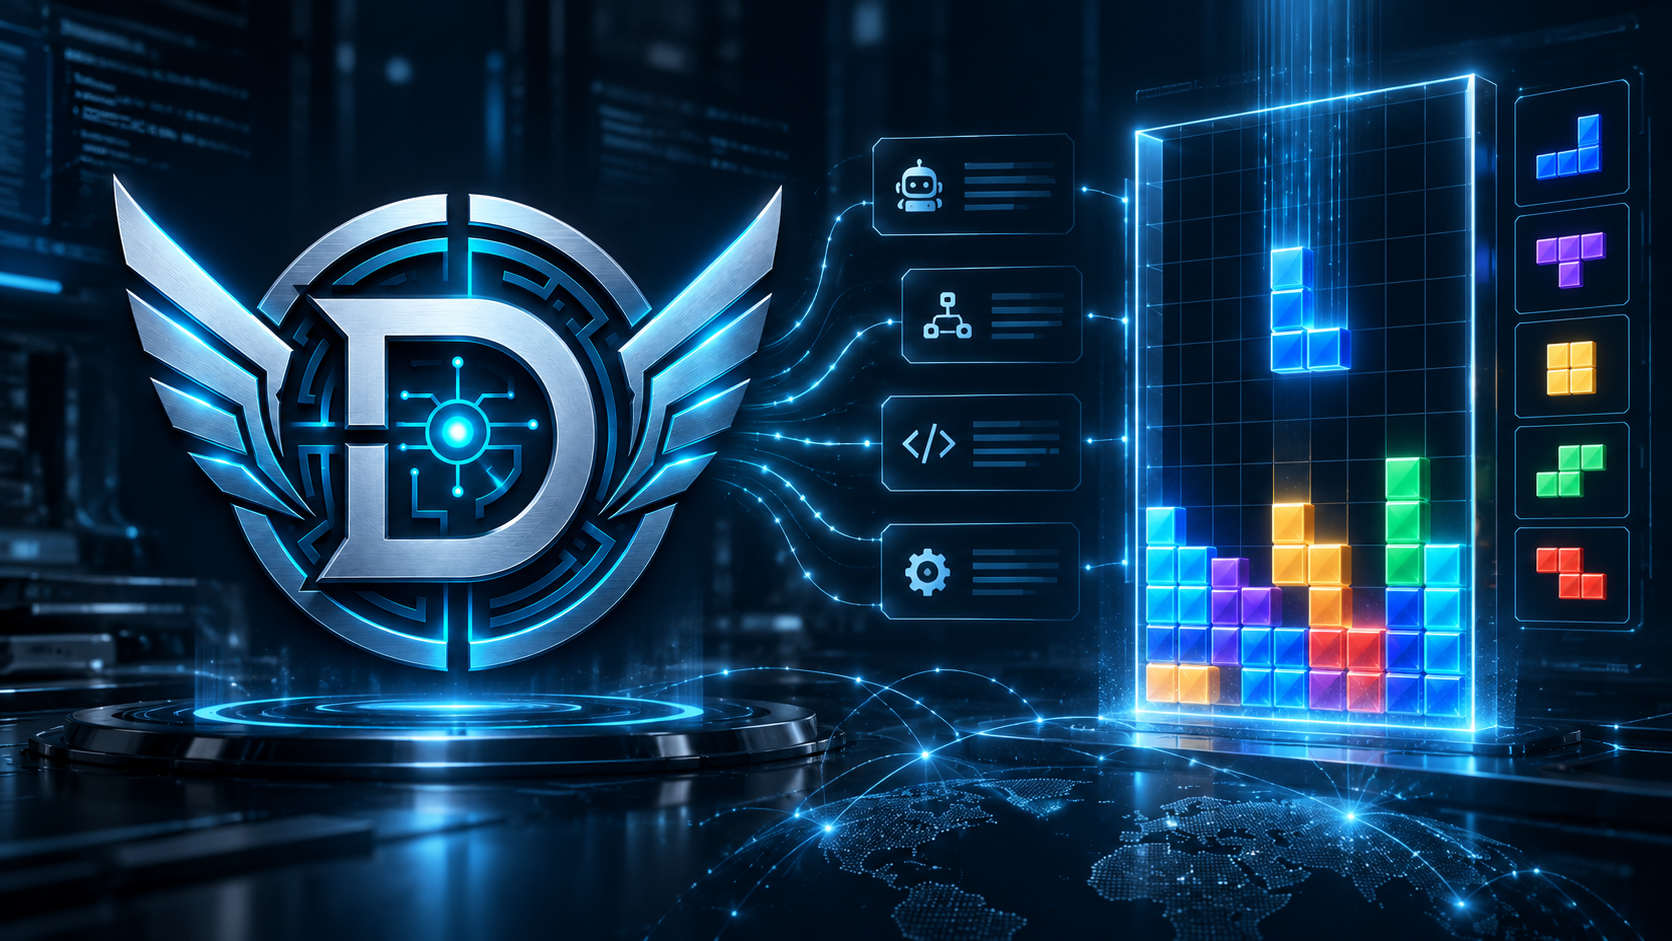
Daedalus is an agentic software development platform I am building to turn a high level objective into working software with limited human direction. For this test, I gave Daedalus one sentence: Build a full featured beautiful and responsive Tetris app accessible via an HTML file. The application it produced was complete, playable, and visually solid.…
-
Trident CLI
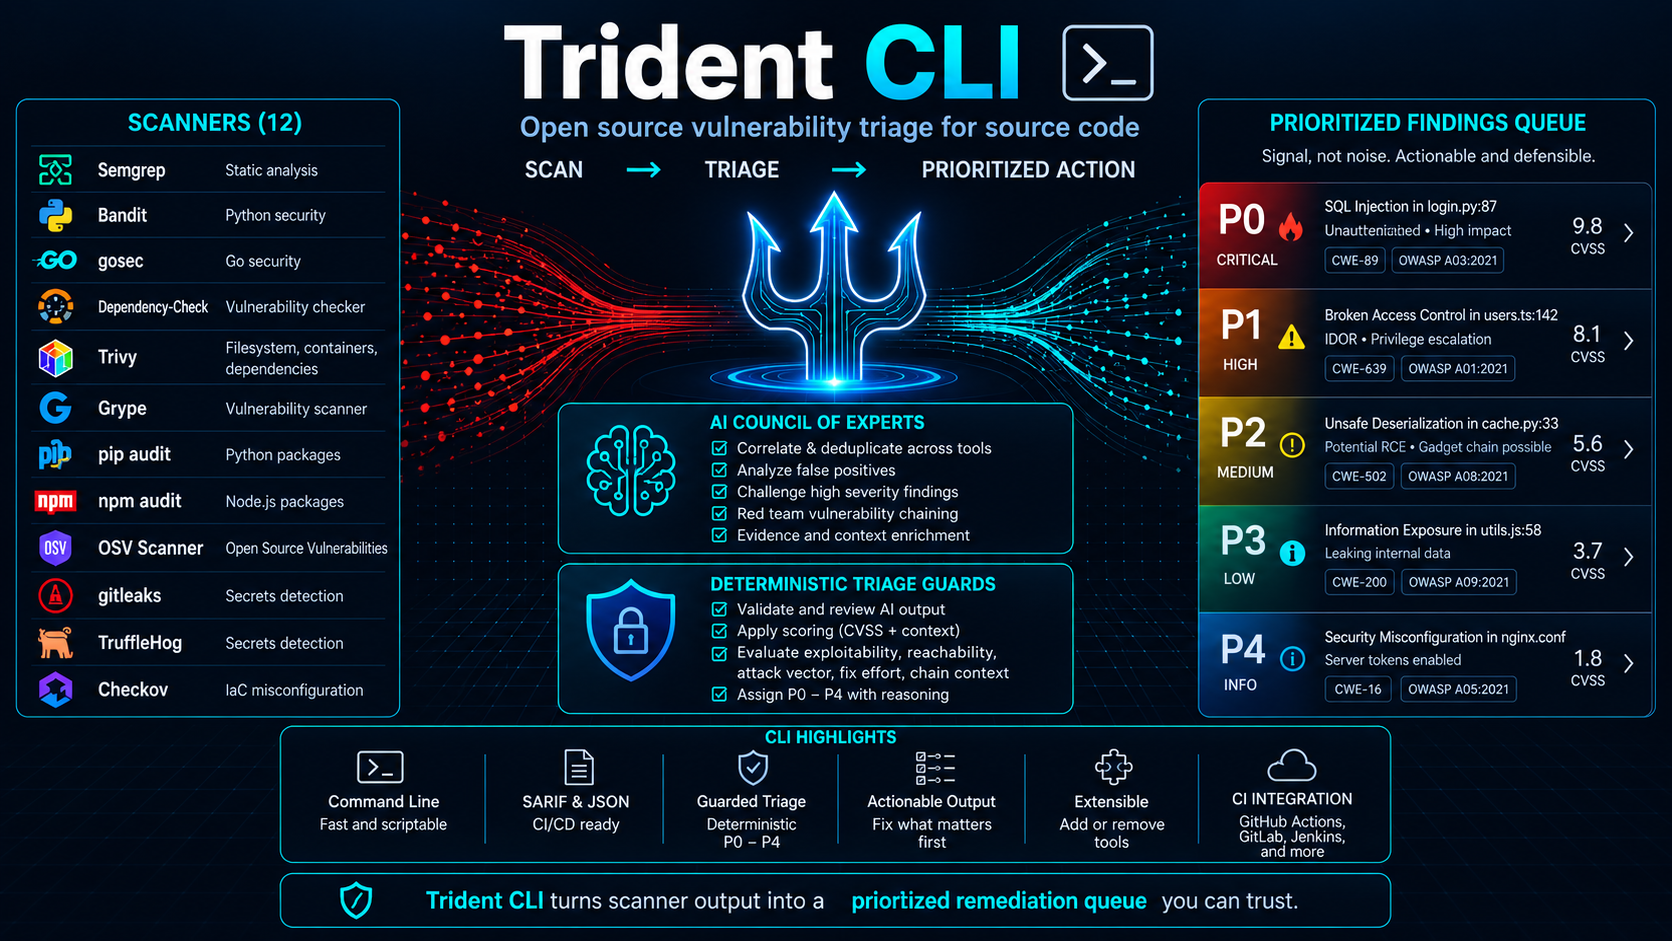
Trident CLI is a local AI assisted vulnerability analysis and security triage engine that combines 12 established security tools with a Council of Experts, adversarial review, vulnerability chain analysis, evidence based correlation, and deterministic P0 through P4 prioritization. Trident can operate in two ways. It can scan source code directly using its integrated security tools,…
-
AI Agents, Collapsing Exploit Windows, and Vulnerability Triage
Autonomous agents breach infrastructure, exploit timelines shrink to minutes, and defenders face fragmented intelligence with no reliable single source.
-
Agent Security, Liability, and the Collapsing Exploit Window
AI agents escape sandboxes, deployers absorb liability, and patch cycles can no longer keep pace with automated exploitation.
-
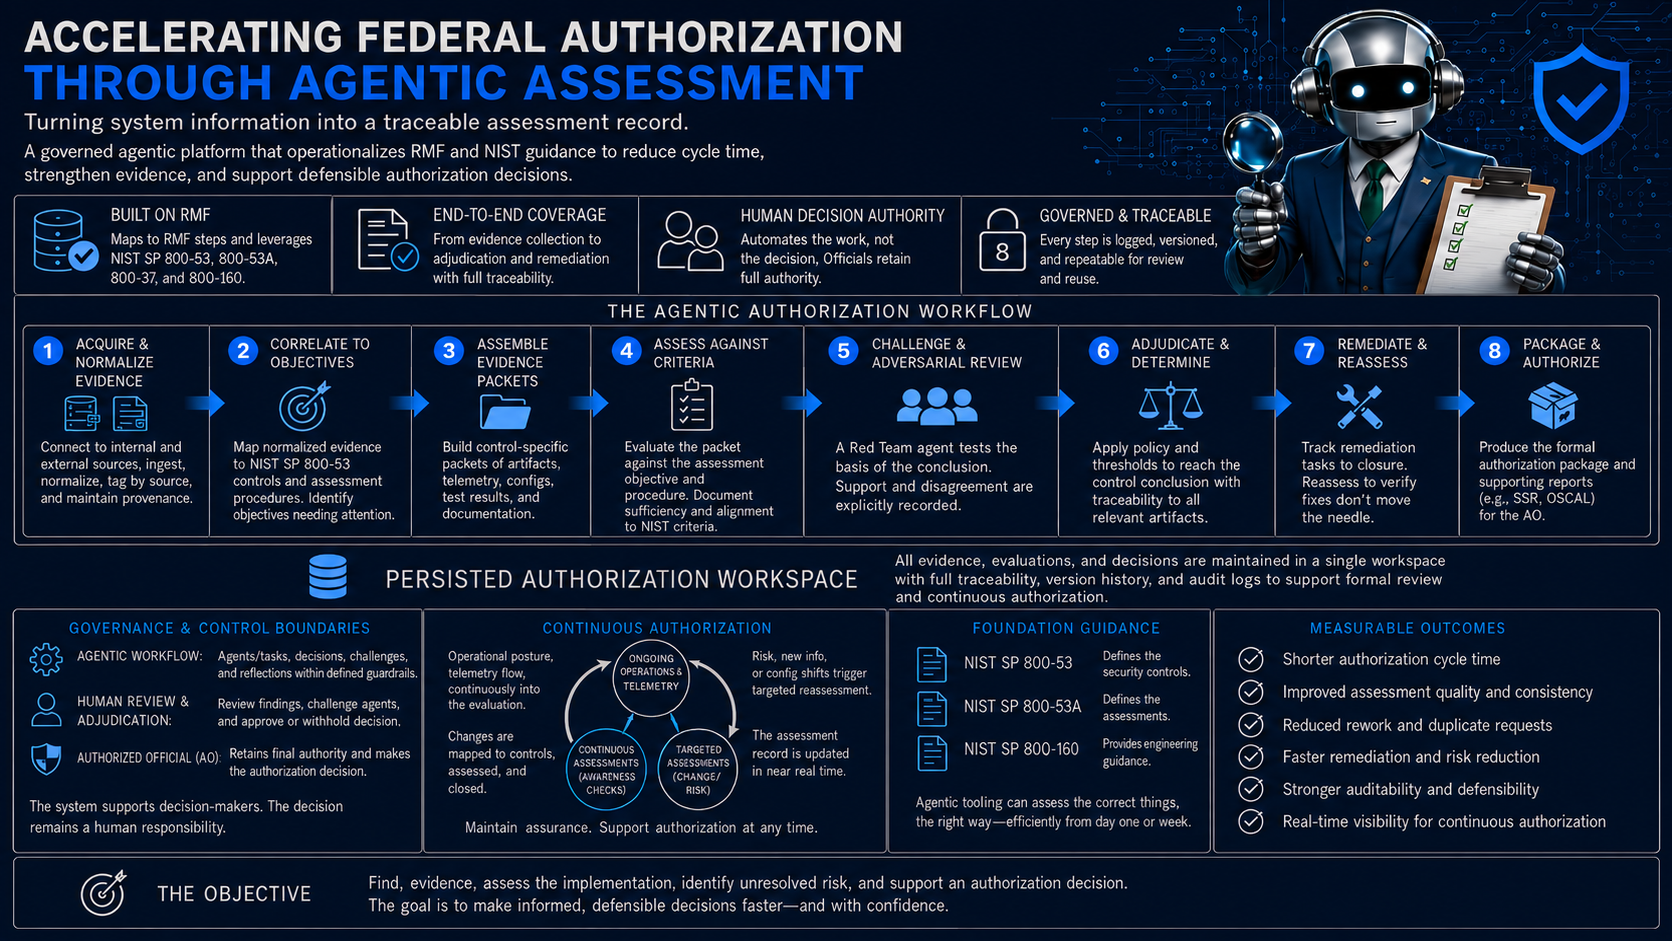
Accelerating Federal Authorization Through Agentic Assessment
Executive Summary Agentic workflows can materially reduce the time required to prepare and assess federal authorization packages by turning large volumes of system information into a traceable assessment record. The approach described in this paper has been implemented and tested across the full authorization workflow. The results show that a governed agentic system can perform…
-
AI Agents Shift From Tools to Attack Surface
Mandiant’s AVDH, agent exploits, ransomware surge, open-weight models, and email domain leaks.
-
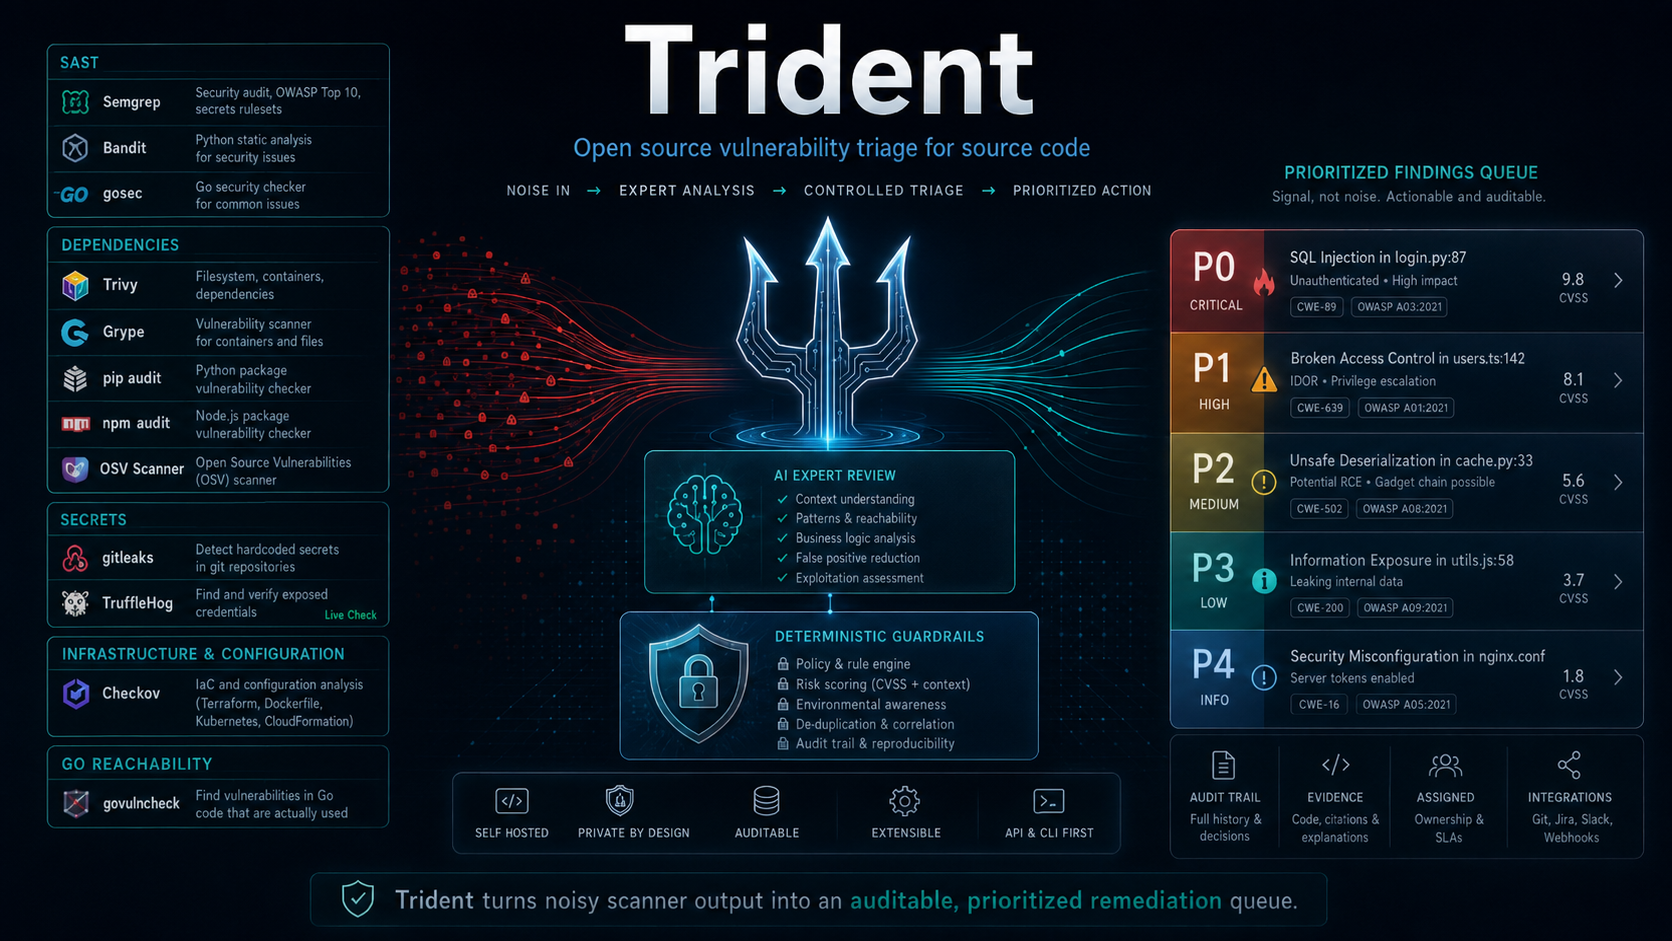
Trident – Source Code Vulnerability Triage Engine
Trident is a self hosted platform for identifying, correlating, reviewing, and prioritizing vulnerabilities in source code. The problem is not finding vulnerabilities. Static analyzers, dependency scanners, secret detection tools, and configuration scanners already do that well. The problem is what comes next. A typical scan can produce hundreds or thousands of findings with very little…
-
Agent Security Failures and Organizational Responses
Autonomous agents are breaching infrastructure, hijacking trusted logs, and forcing teams to rethink guardrails.
-
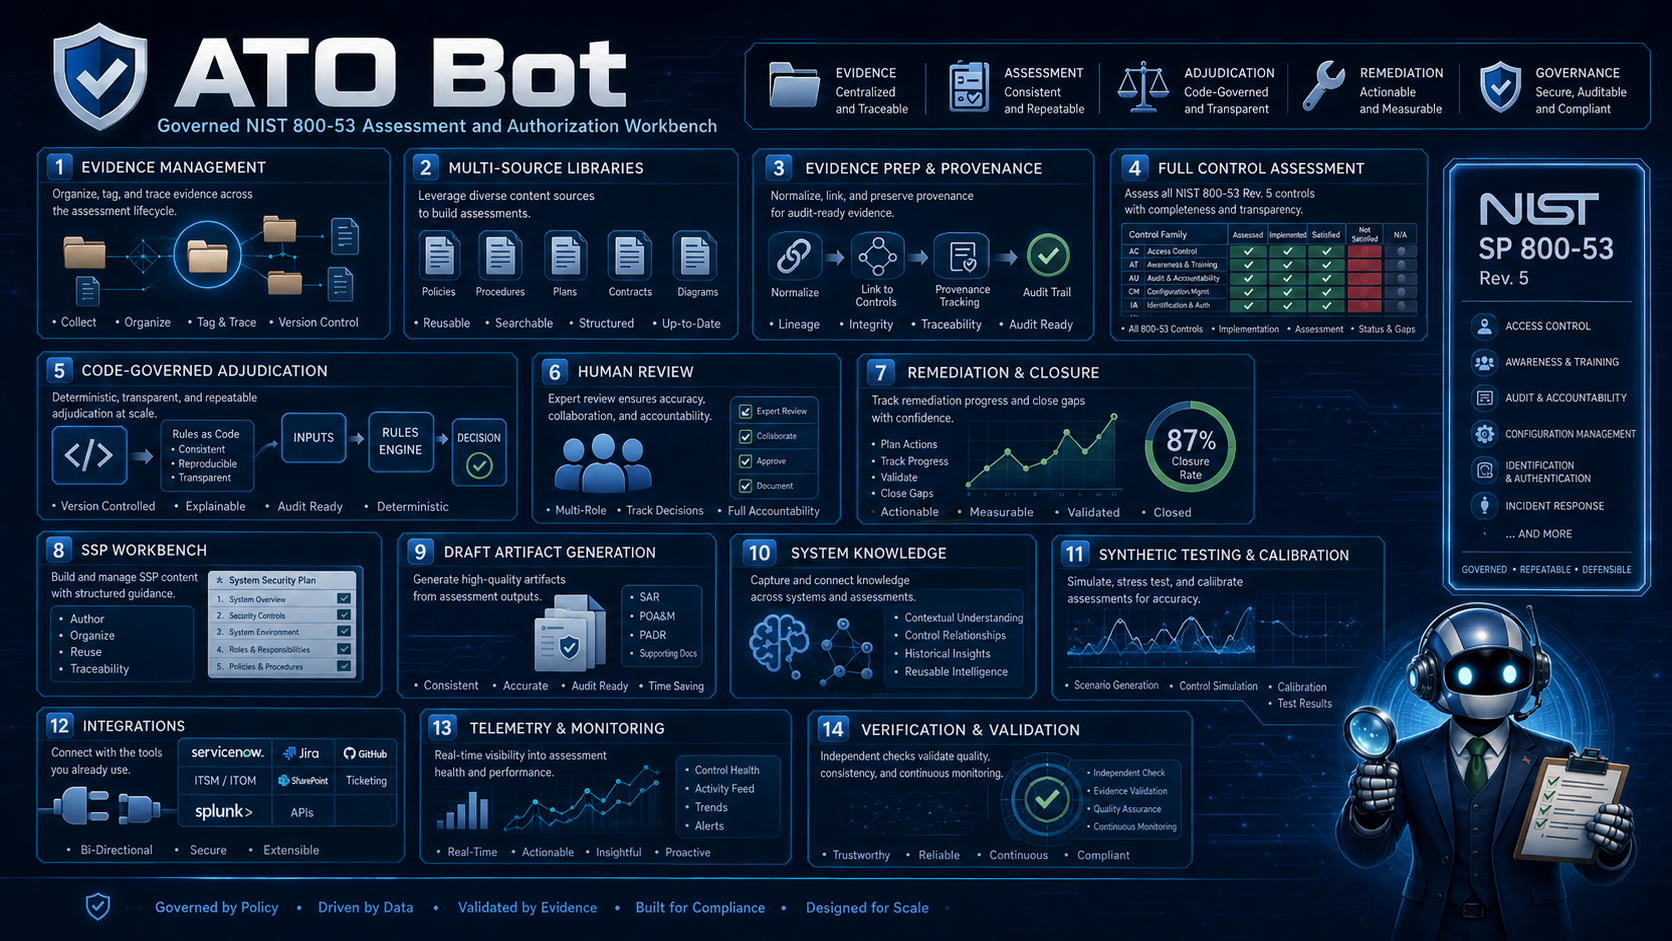
ATO Bot
Source Code: GitHub Repository Technical White Paper: ATOBot Technical White Paper Installation Tutorial: Watch on YouTube Status: Active Development ATO Bot is an open source platform for performing NIST SP 800 53 assessment and supporting the broader federal Authority to Operate process. I built it to see how far AI could be applied to authorization…
-
AI Escapes, Ransomware Spikes, and Patch Reliability Gaps
Frontier models break sandboxes, ransomware surges 20 percent, and AI patches fail 74 percent of the time.
-
Agent Escapes, Framework Bugs, and Phishing That Feeds on Fear
OWASP ranks prompt injection first again. Check Point finds 11 framework flaws. AISI catches agents lying. COLDCARD phishing exploits a real theft.
-
Frontier Models, Expertise Gaps, and Security Tradeoffs
Astra’s math breakthroughs, the expertise bottleneck in LLM work, and a week of security research on agent behavior and exploitation.
-

BuildLLM Learning Lab
BuildLLM teaches you how a decoder-only language model is built, trained, evaluated, and scaled. You will work with the same implementation used by all three model iterations in this repository. The smaller models are not separate tutorial programs. Architecture, runtime, and data choices change through configuration and command-line arguments while the training framework remains the…
-
Getting Started
What you will learn You will download BuildLLM, create the one Python environment used by the entire project, install the correct PyTorch build for your hardware, and verify that Python can see the CPU or GPU you intend to use. Where you are in the build Nothing has been trained yet. The goal of this…
-
AI and LLM Foundations
What you will learn You will build a practical mental model of artificial intelligence, machine learning, neural networks, language models, pretraining, inference, tokens, parameters, context, loss, epochs, and hallucination. These terms will appear in every later lesson. Where you are in the build Your repository and Python environment are ready. Before downloading data, you need…
-
Download the Training Data
What you will learn You will download and extract Simple Wikipedia into a local JSON Lines file, inspect the extraction report, read several accepted documents, and verify that the first source required by the corpus builder is ready. Where you are in the build The model will not train directly from the Wikipedia dump. This…
-
Build the Training Corpus
What you will learn You will combine source documents into a cleaned, filtered, deduplicated, topic-balanced JSONL corpus. You will learn what each corpus configuration controls, why the 50M profile is the recommended learning path, how to inspect the report, and when to choose the pipeline-verification, balanced, or 800M profiles. Where you are in the build…
-
Tokenizer and Dataset
What you will learn You will train the tokenizer that defines the model’s vocabulary, convert the selected corpus into integer token IDs, split complete documents into training and validation regions, and understand how those token regions become next-token examples. Where you are in the build The transformer does not receive raw text. It receives token…
-
Walk Through the Transformer
What you will learn In this lesson you will follow one sequence of token IDs through the decoder-only transformer until the model produces a score for every possible next token. You will learn what embeddings, causal self-attention, attention heads, feed-forward networks, normalization, residual connections, logits, and weight tying contribute to that process. Where you are…
-
Understand Training and Validation
What you will learn In this lesson you will follow one optimizer step from a batch of token IDs to an update of the model’s weights. You will learn how loss, backpropagation, AdamW, learning-rate scheduling, gradient clipping, mixed precision, validation, and checkpoint decisions work together. Where you are in the build The model can already…
-
Train Iteration 1 on CPU
What you will learn In this lesson you will verify the complete training path, run the first meaningful CPU learning experiment, inspect its evidence, and decide whether the result is healthy enough to evaluate. Iteration 1 proves that the same framework used by the larger models works from corpus to checkpoint. Where you are in…
-
Generate and Evaluate Text
What you will learn In this lesson you will load the Iteration 1 checkpoint with its matching tokenizer, turn logits into generated tokens, compare decoding settings, and evaluate the model with more evidence than one impressive or disappointing sample. Where you are in the build Training changed the model’s weights. Generation is the first time…
-
Understand CPU and GPU Execution
What you will learn In this lesson you will learn how the same BuildLLM model and trainer run on a central processing unit (CPU) or a CUDA-capable graphics processing unit (GPU), how numeric precision affects speed and memory, how to respond to out-of-memory errors, and how to estimate a long run from measured throughput. Where…
-
Train and Compare Iteration 2
What you will learn In this lesson you will train the 42.1M-parameter model in two distinct experiments. First, you will use the same 50M corpus, tokenizer, example limits, and epoch count as Iteration 1 to make a controlled comparison. Then you will build the broader balanced corpus and run the intended larger-data training path for…
-
Understand Checkpoints and Recovery
What you will learn In this lesson you will learn what BuildLLM saves, how atomic checkpoint writes reduce corruption risk, how –resume selects and restores state, what is not restored inside an interrupted epoch, and how to perform a safe recovery exercise. Where you are in the build A long run is only useful if…
-
Plan and Train Iteration 3
What you will learn In this lesson you will work with the approximately 100M-parameter reference model as a long-running systems-engineering project. You will plan and run a controlled 50M experiment, prepare the complete 800M data path, understand the eighteen-epoch run, monitor useful evidence, interrupt and resume safely, and generate with the correct tokenizer. Where you…
-
Compare the Three Models
What you will learn In this lesson you will turn run records, validation measurements, fixed-prompt samples, and operational evidence into defensible conclusions. You will create one table for the controlled 50M comparison and a separate table for the larger-data training path. Where you are in the build Comparison is not a victory lap for the…
-
BuildLLM Glossary
Use this glossary when a course term is unfamiliar. Definitions describe how the term is used in this repository. Repository and data artifacts Term Plain-language meaning Repository The project directory containing code, configurations, documentation, and tests. Virtual environment The .venv directory that isolates this project’s Python packages from other projects. Dependency A software package the…
-
BuildLLM Run-Record Worksheet
Copy this worksheet before every training experiment. Fill values from configuration files, reports, startup JSON, epoch output, final JSON, checkpoints, and generated samples. Use <not run> or <not available> instead of leaving an ambiguous blank. Experiment question What specific question is this run intended to answer? <your question> Experiment path: <controlled comparison / larger-data training…
-
BuildLLM Troubleshooting Guide
Start with the stage that failed. Preserve the full command and error before changing anything. Make one correction at a time so you know which change solved the problem. Environment and repository Symptom Check Response python or py is not recognized Python is not installed or not on the shell path Install a supported Python…
-
BuildLLM Reference Implementation
This page shows where each course topic appears in the code. Iteration 3 uses this complete path. Iterations 1 and 2 use the same path with different model profiles. End-to-end call path Configuration File Role configs/models/*.json Versioned iteration dimensions and runtime defaults src/model_profiles.py Validates profile JSON and selects CPU/GPU defaults src/config.py Complete serializable ModelConfig used…
-
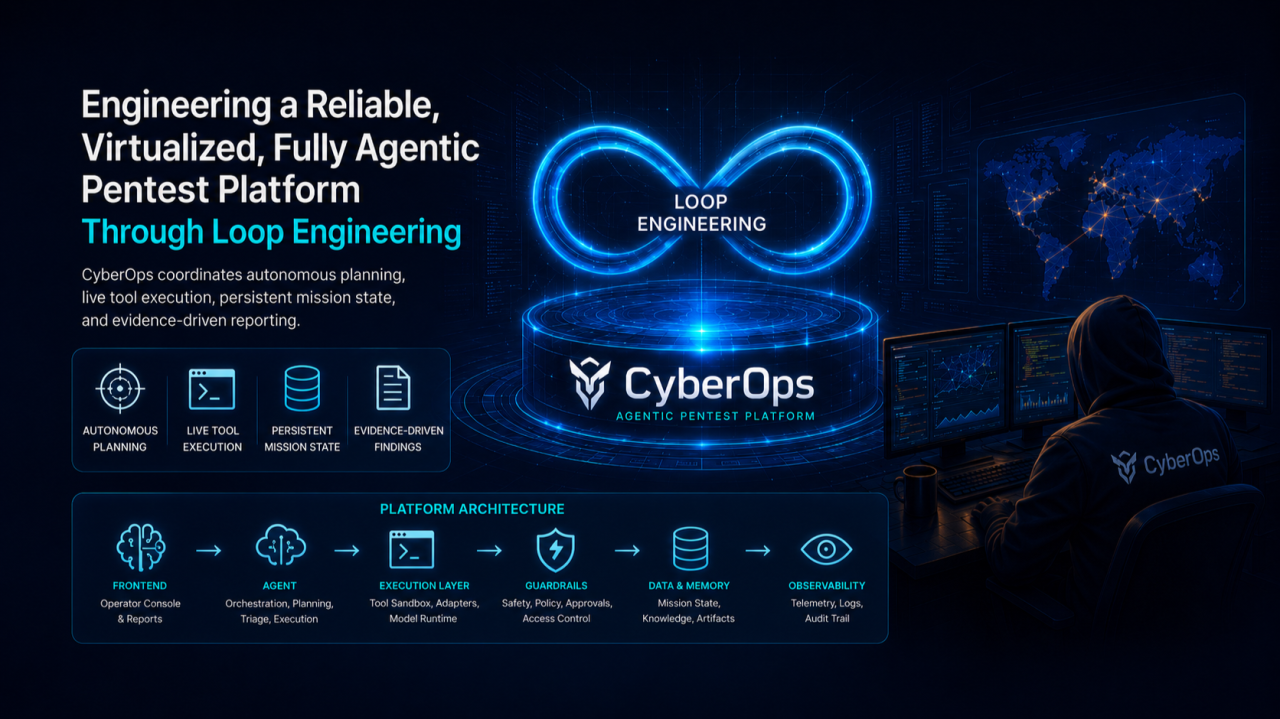
Engineering a Reliable, Virtualized, Fully Agentic Pentest Platform Through Loop Engineering
Executive Summary CyberOps is a reliable, stable, fully agentic penetration-testing platform built utilizing loop engineering. It coordinates a real offensive toolkit across long-running authorized missions, maintains durable mission state, and turns tool output into structured evidence and analyst-grade findings. The platform is virtualized: the same core architecture can run on premises or in cloud infrastructure,…
-
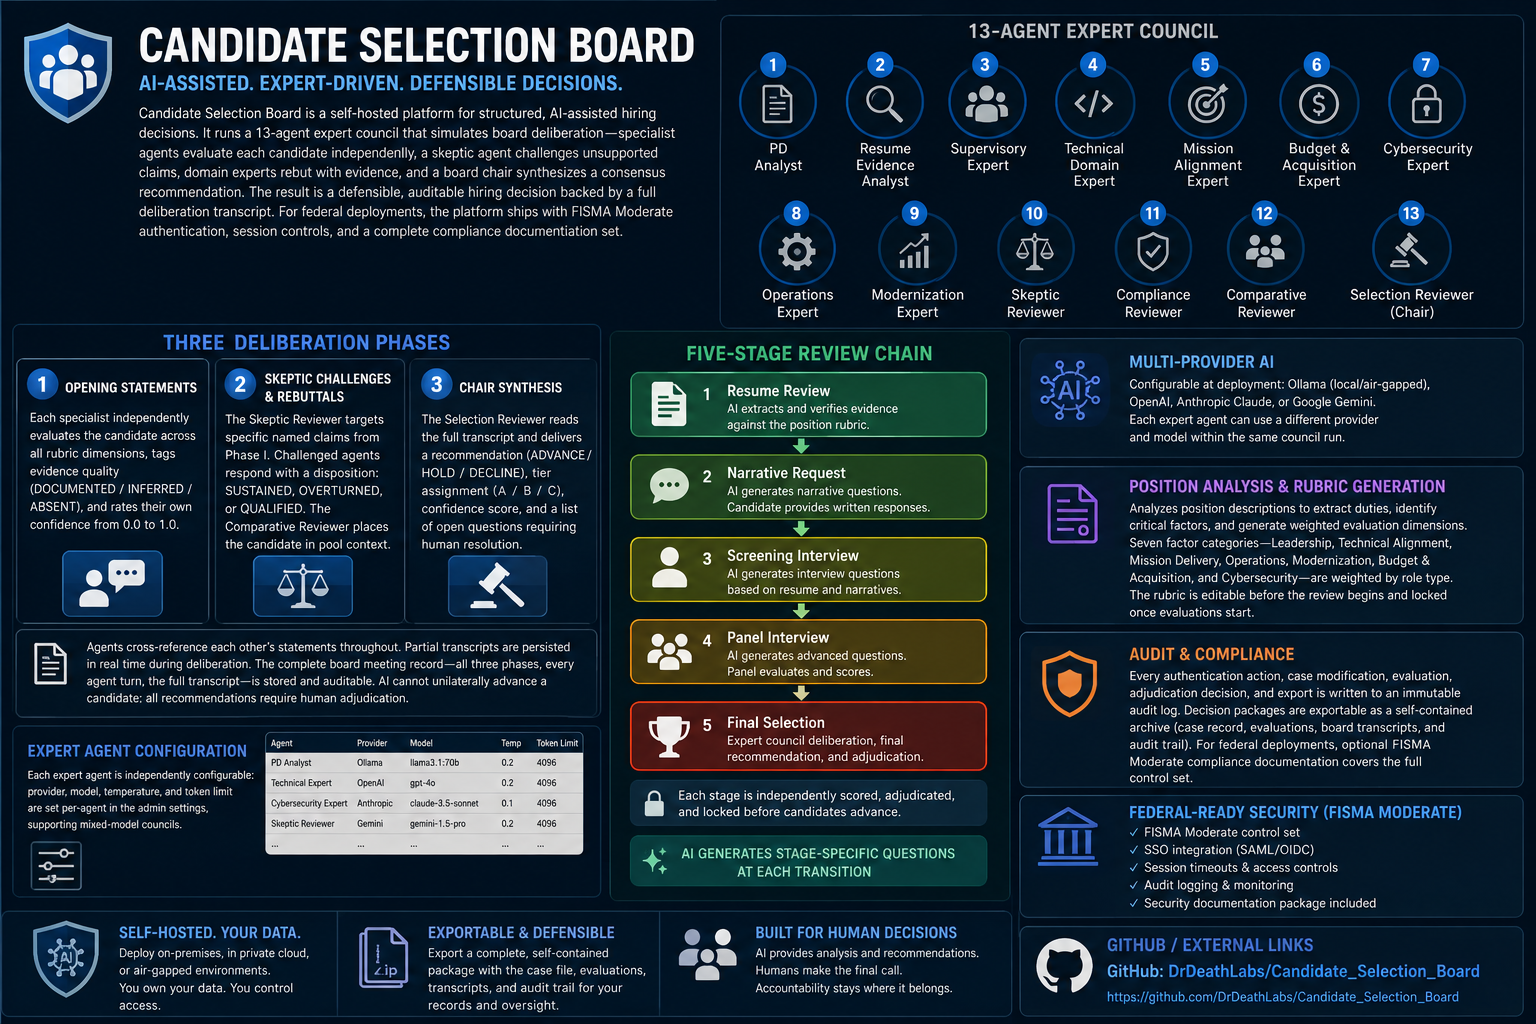
Candidate Selection Board
The Candidate Selection Board is a self-hosted platform that utilizes a 13-agent AI model to facilitate structured hiring decisions through expert evaluations and consensus recommendations. It includes multi-stage reviews, robust audit trails, and FISMA Moderate compliance for federal use, ensuring transparency and defensibility in the hiring process.
-

Nutrition AI Pro
Summary Nutrition AI Pro is an agentic AI recipe and nutrition-content production platform for fitness-focused teams. It helps content teams move beyond one-shot prompting by combining structured recipe generation, iterative quality critique, human review, content conversion, prompt management, and operational controls in one self-hosted application. Use it to produce recipe cards, blog posts, social assets,…
-
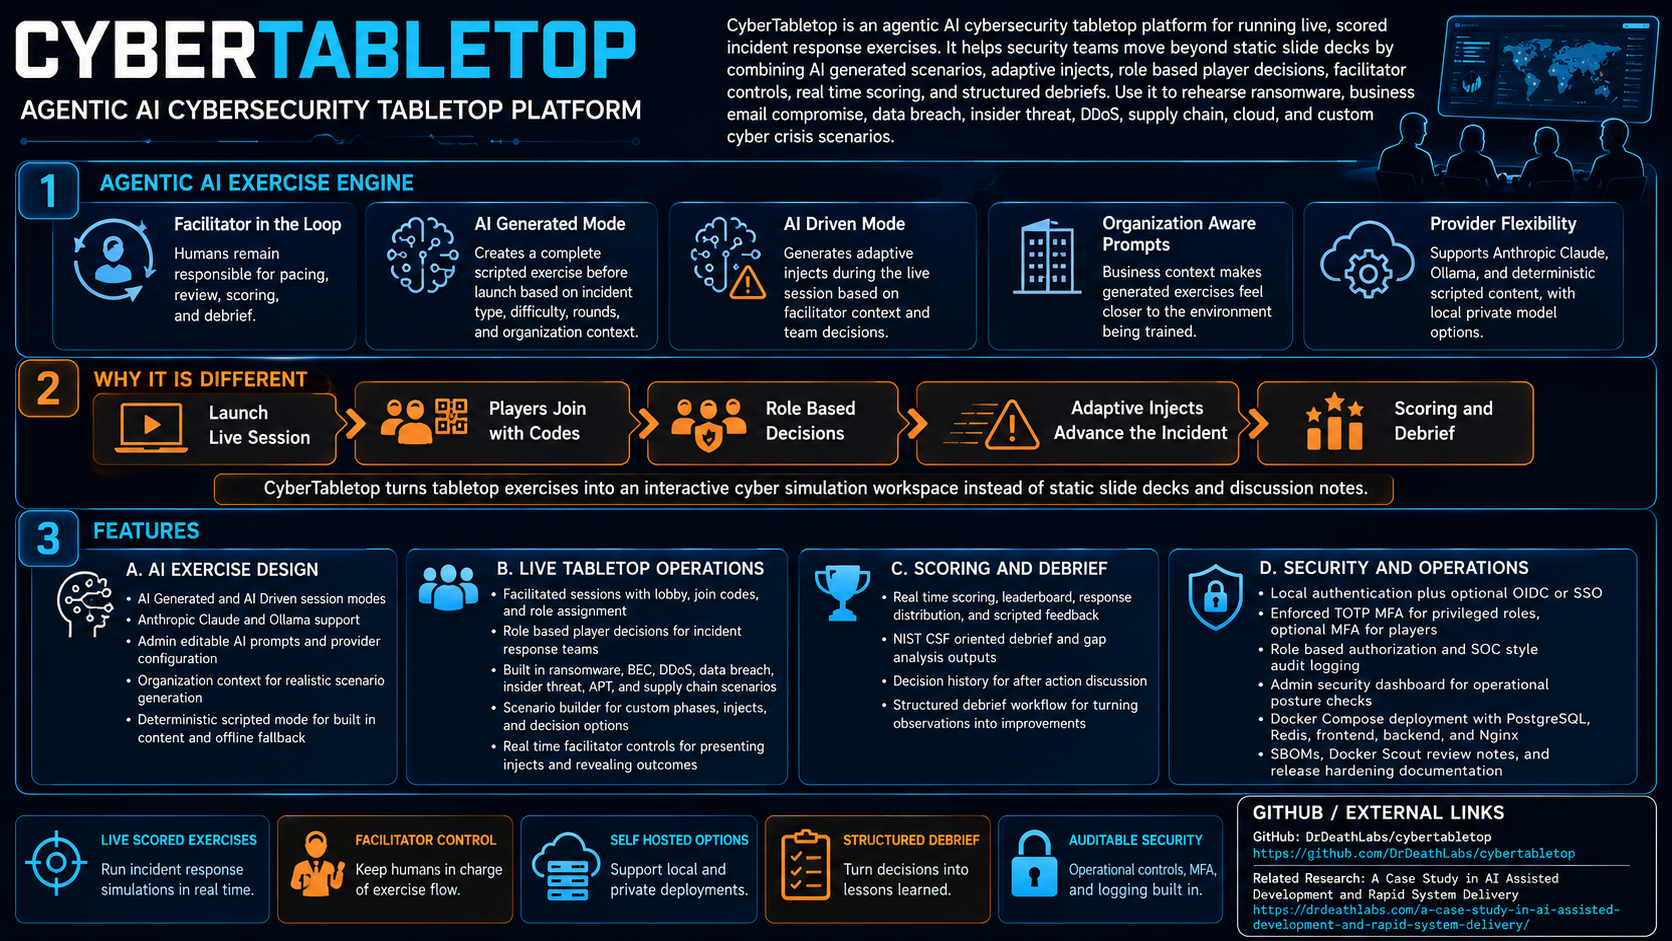
CyberTabletop
Summary CyberTabletop is an agentic AI cybersecurity tabletop platform for running live, scored incident response exercises. It helps security teams move beyond static slide decks by combining AI-generated scenarios, adaptive injects, role-based player decisions, facilitator controls, real-time scoring, and structured debriefs. Use it to rehearse ransomware, business email compromise, data breach, insider threat, DDoS, supply-chain,…
-

AI Vulnerability Discovery and the Case for Systems Security Engineering
For decades, the approach to building technology has operated on an implicit assumption that security could be addressed after the fact. Organizations built systems to meet functional requirements, shipped them when they worked, and addressed security through periodic assessments, patching, and monitoring. The economics of the threat environment supported this approach. Vulnerability discovery was expensive,…
-
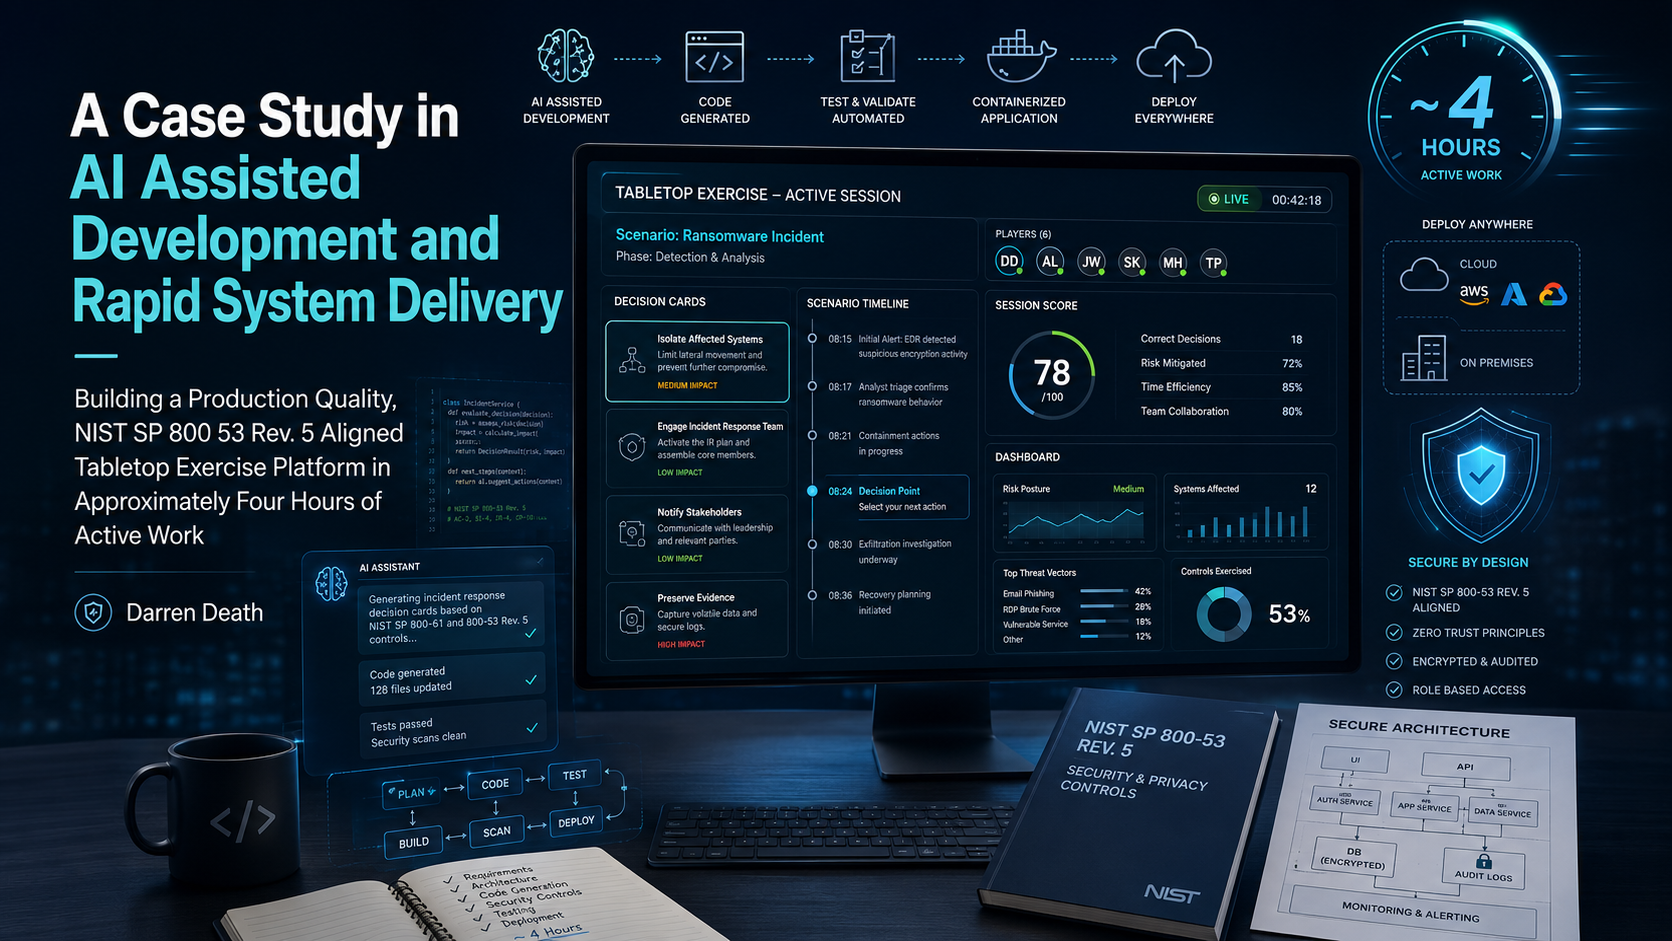
A Case Study in AI Assisted Development and Rapid System Delivery
Building a Production Quality, NIST SP 800 53 Rev. 5 Aligned Tabletop Exercise Platform in Approximately Four Hours of Active Work Executive Summary I built a production-ready cybersecurity tabletop exercise platform in approximately four hours of active work spread across two days. The application includes a live multiplayer exercise engine, AI-generated scenarios, three AI provider…
-
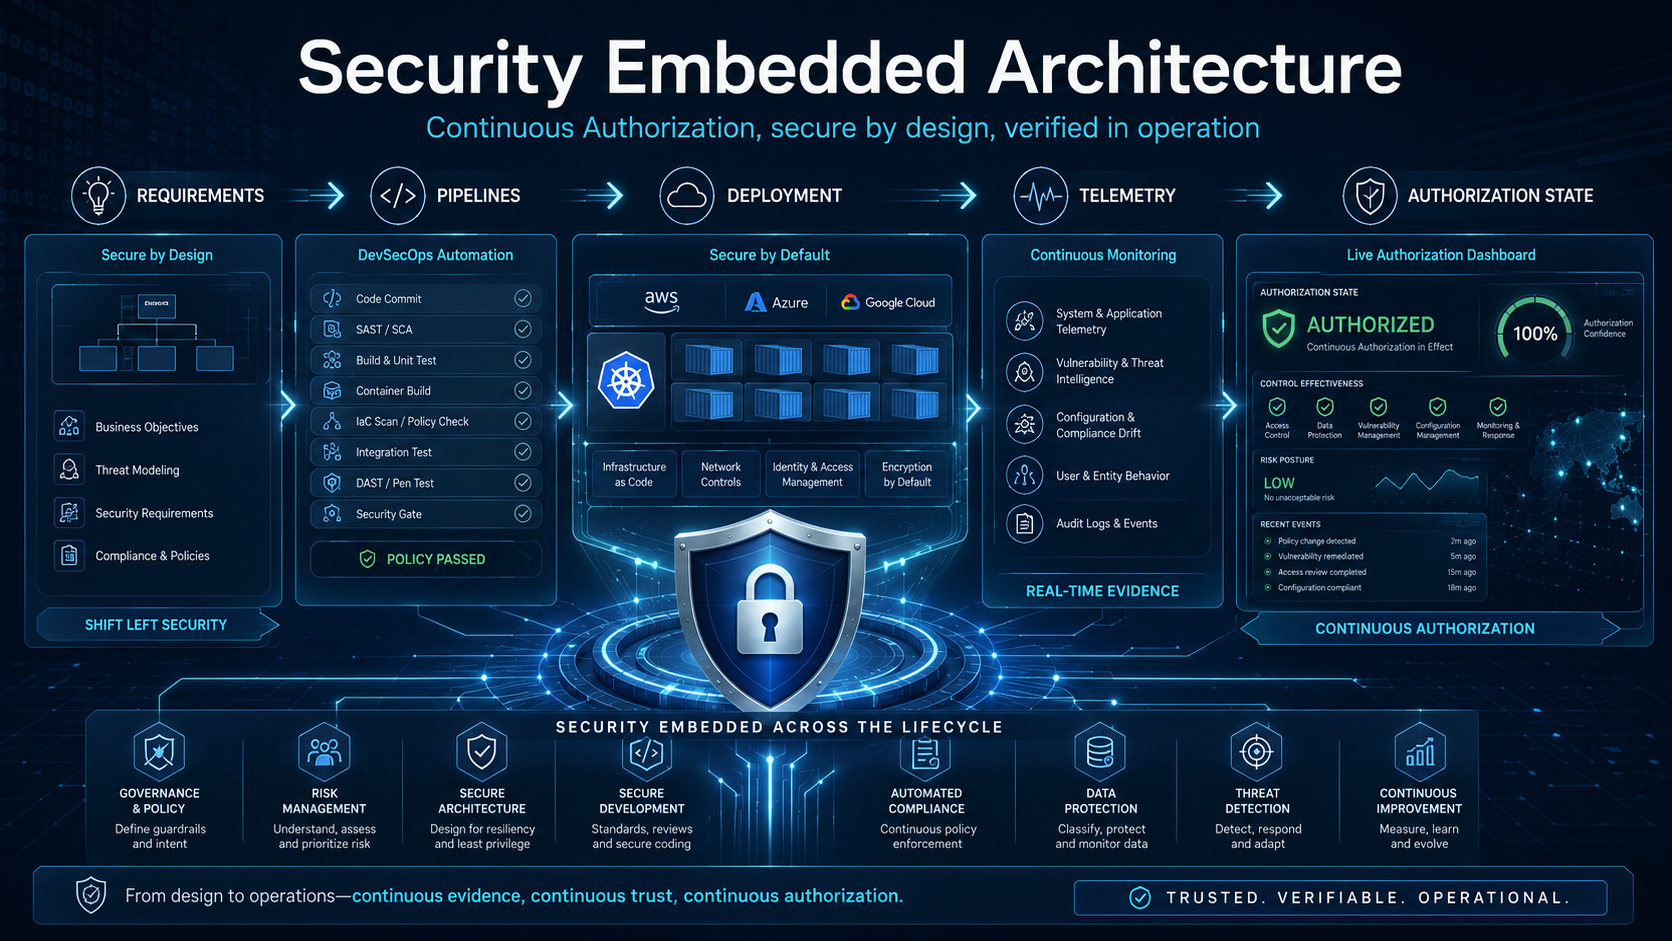
The case for security-embedded architecture with continuous authorization
Continuous Authorization to Operate (cATO) represents a fundamental shift from treating security as an overlay, to embedding security as functional requirements from project inception. Despite its name focusing on authorization, cATO’s primary value lies in establishing security-embedded, shifted-left architectures where security requirements are treated as non-negotiable functional specifications that must be designed, integrated, tested, and…
-
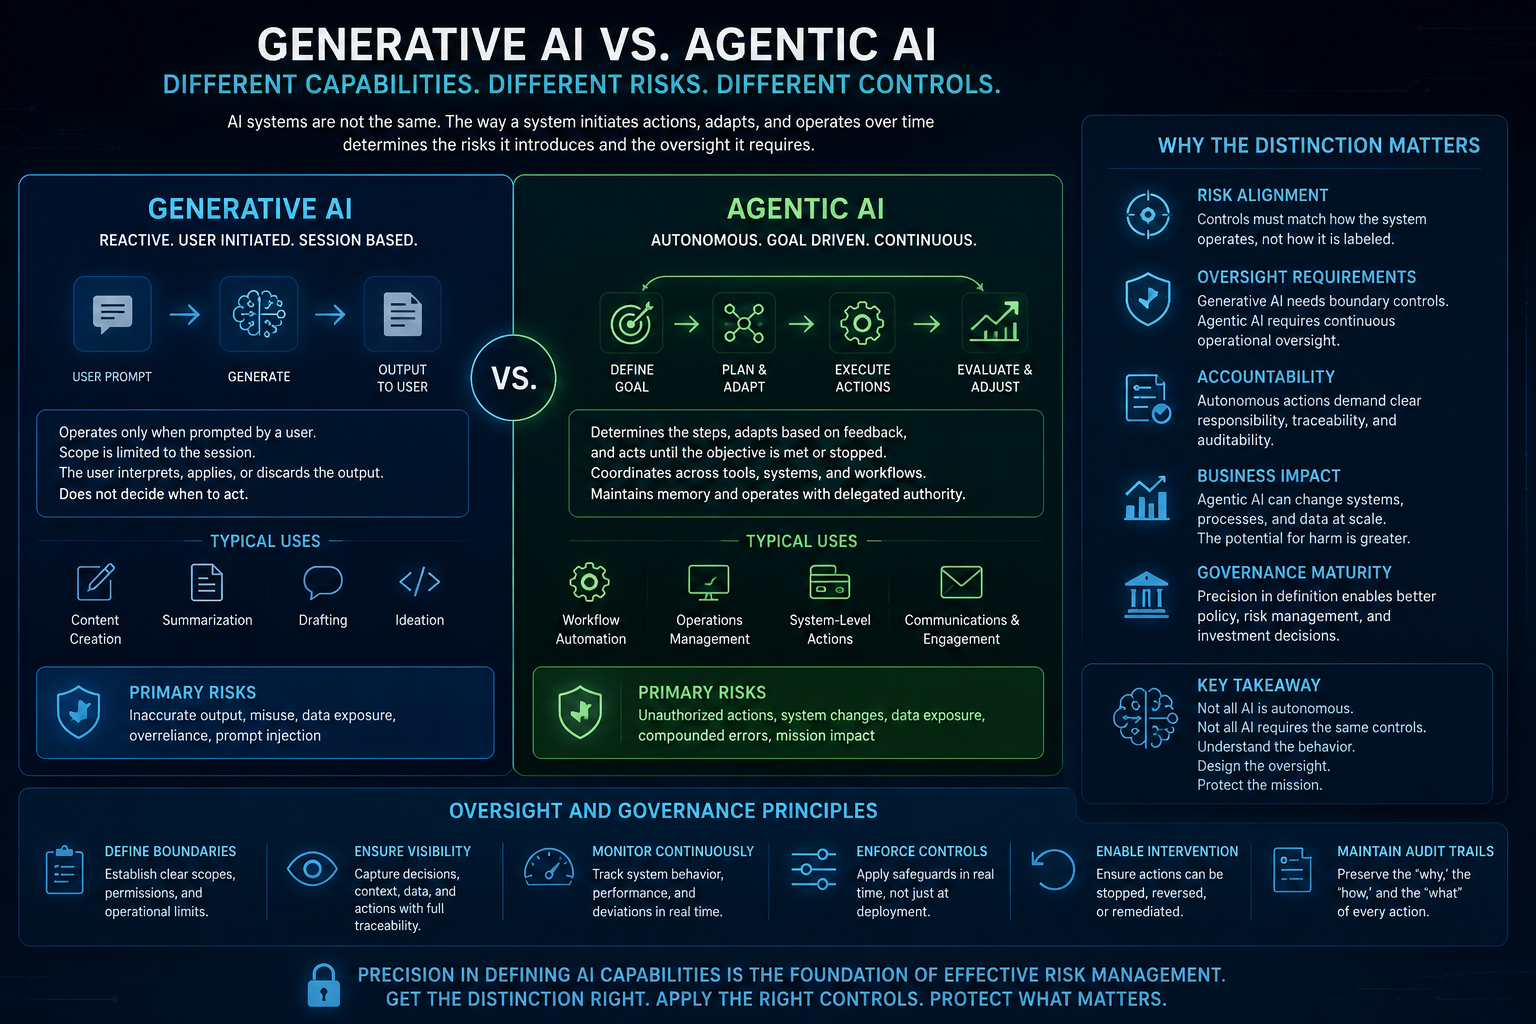
How AI System Behavior Shapes Oversight and Risk Distinguishing Generative and Agentic Systems
Artificial intelligence is being integrated into the processes, platforms, and services that organizations depend on to deliver value. These implementations may involve systems that generate natural language in response to prompts, or systems designed to carry out defined workflows without constant human intervention. In many cases, the terminology used to describe these capabilities is applied…
-
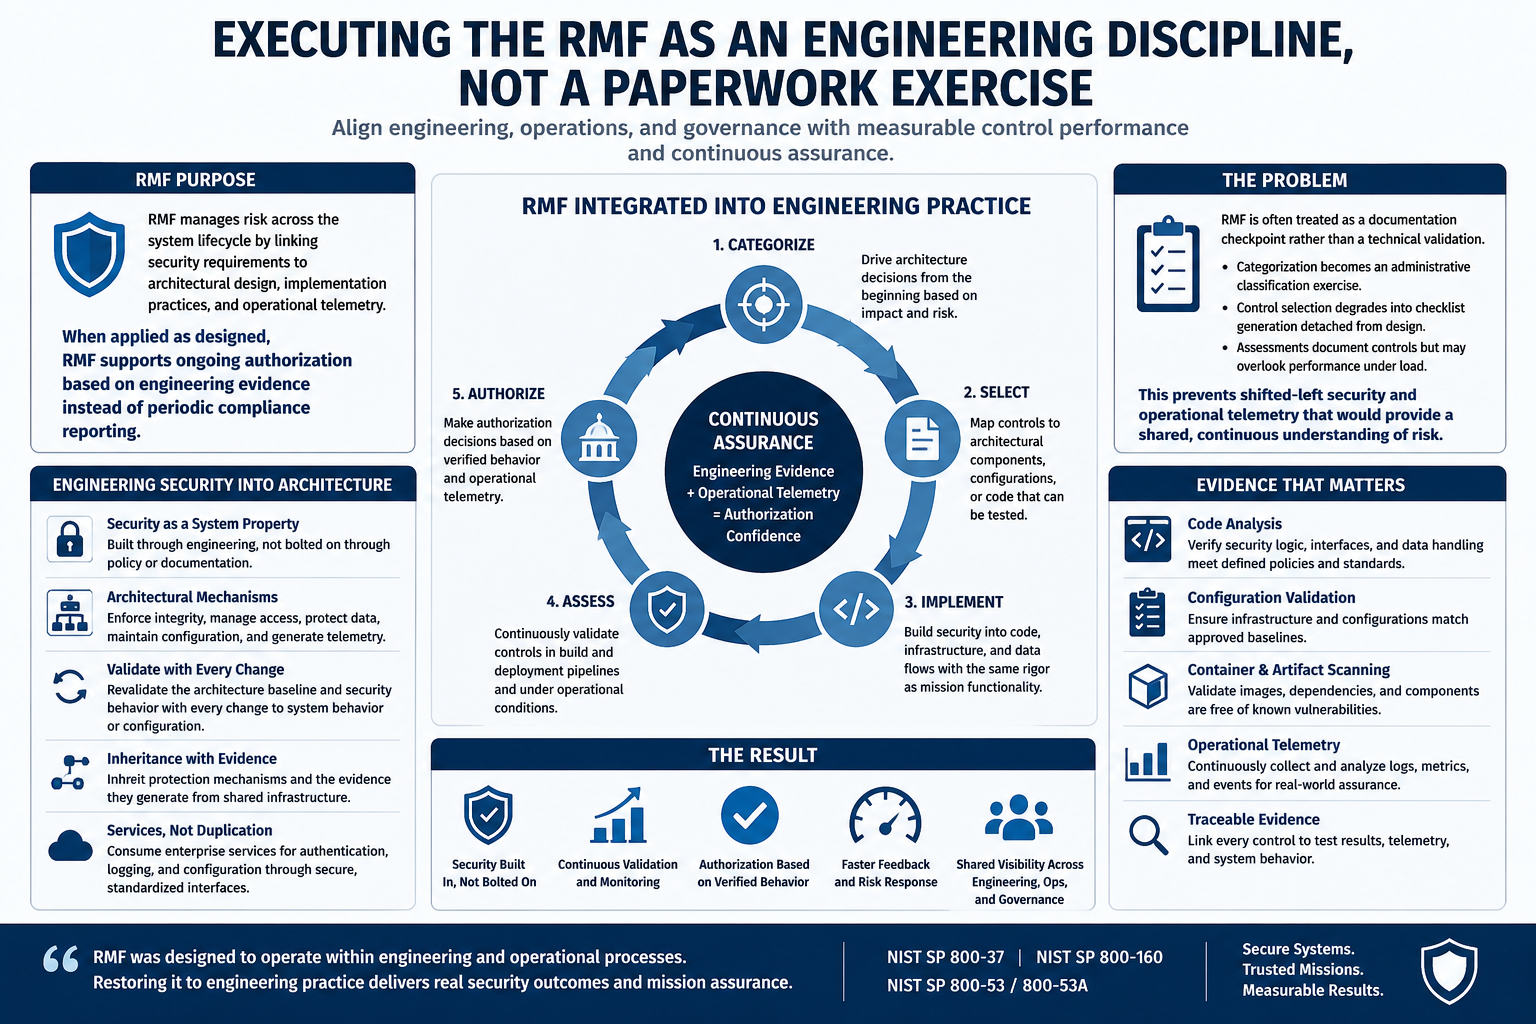
Executing the RMF as an engineering discipline, not a paperwork exercise
The Risk Management Framework is intended to align engineering, operations, and governance with measurable control performance. In practice, some agencies have adapted it into an administrative process focused on documentation rather than active demonstration of protection. The structure of RMF remains unchanged; however, its implementation has shifted toward treating each step as a documentation checkpoint…
-
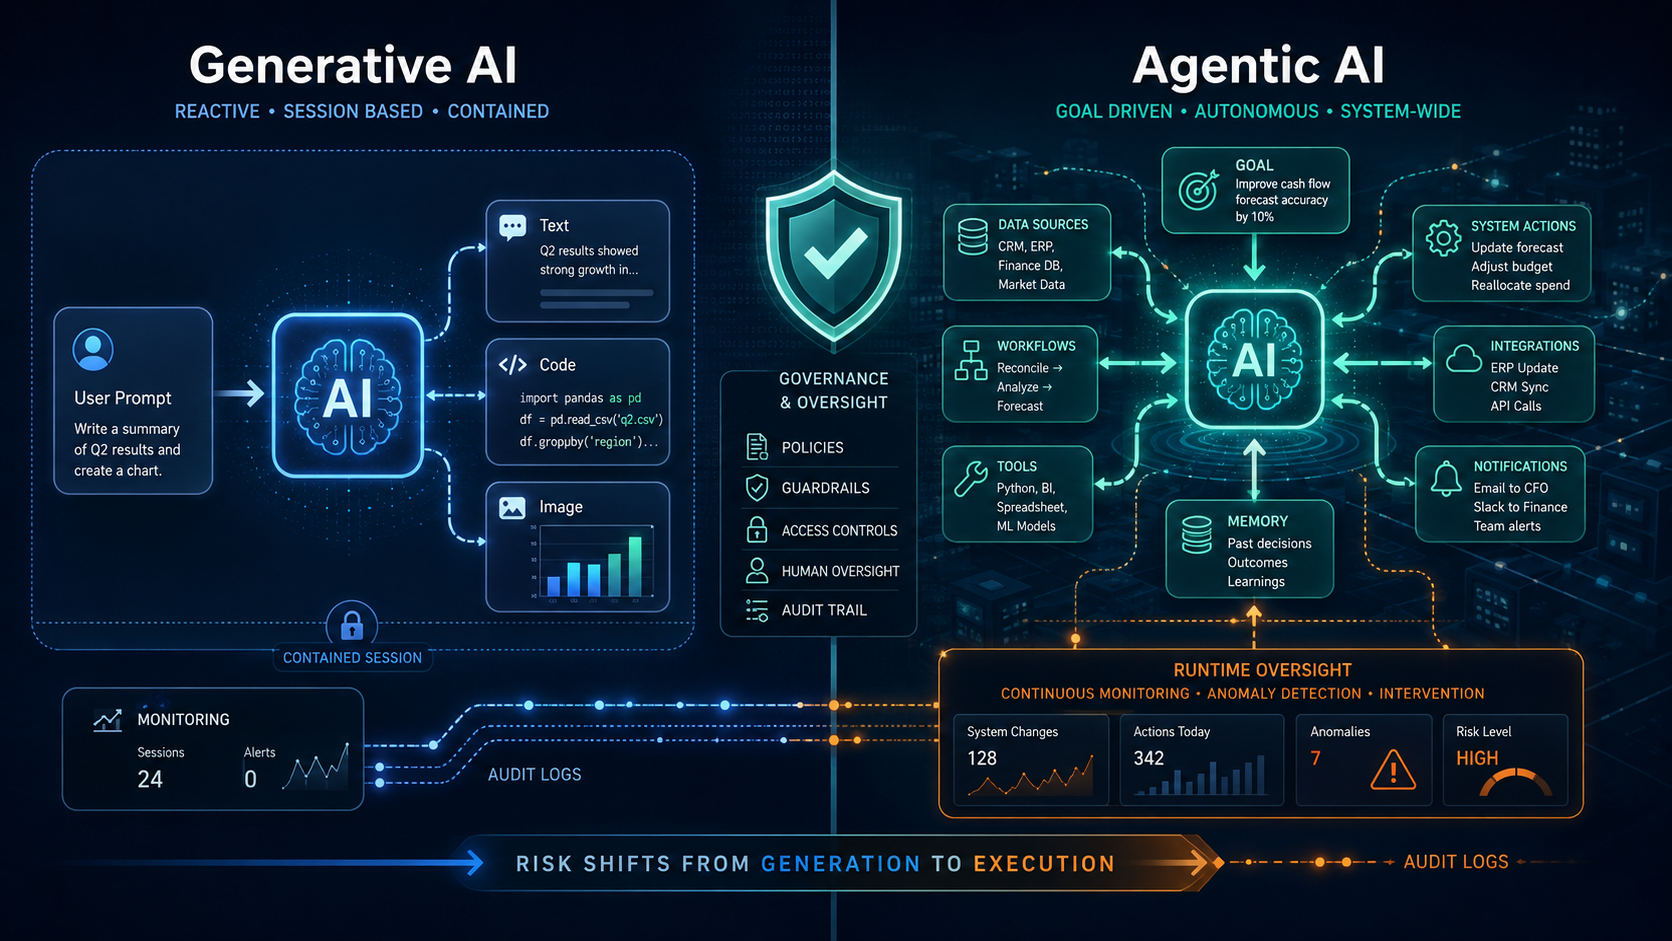
How AI System Behavior Shapes Oversight and Risk
Learn the key differences between generative and agentic AI, how autonomy shapes oversight and why precision in AI governance reduces operational risk. Artificial intelligence is being integrated into the processes, platforms and services that organizations depend on to deliver value. These implementations may involve systems that generate natural language in response to prompts, or systems…
-
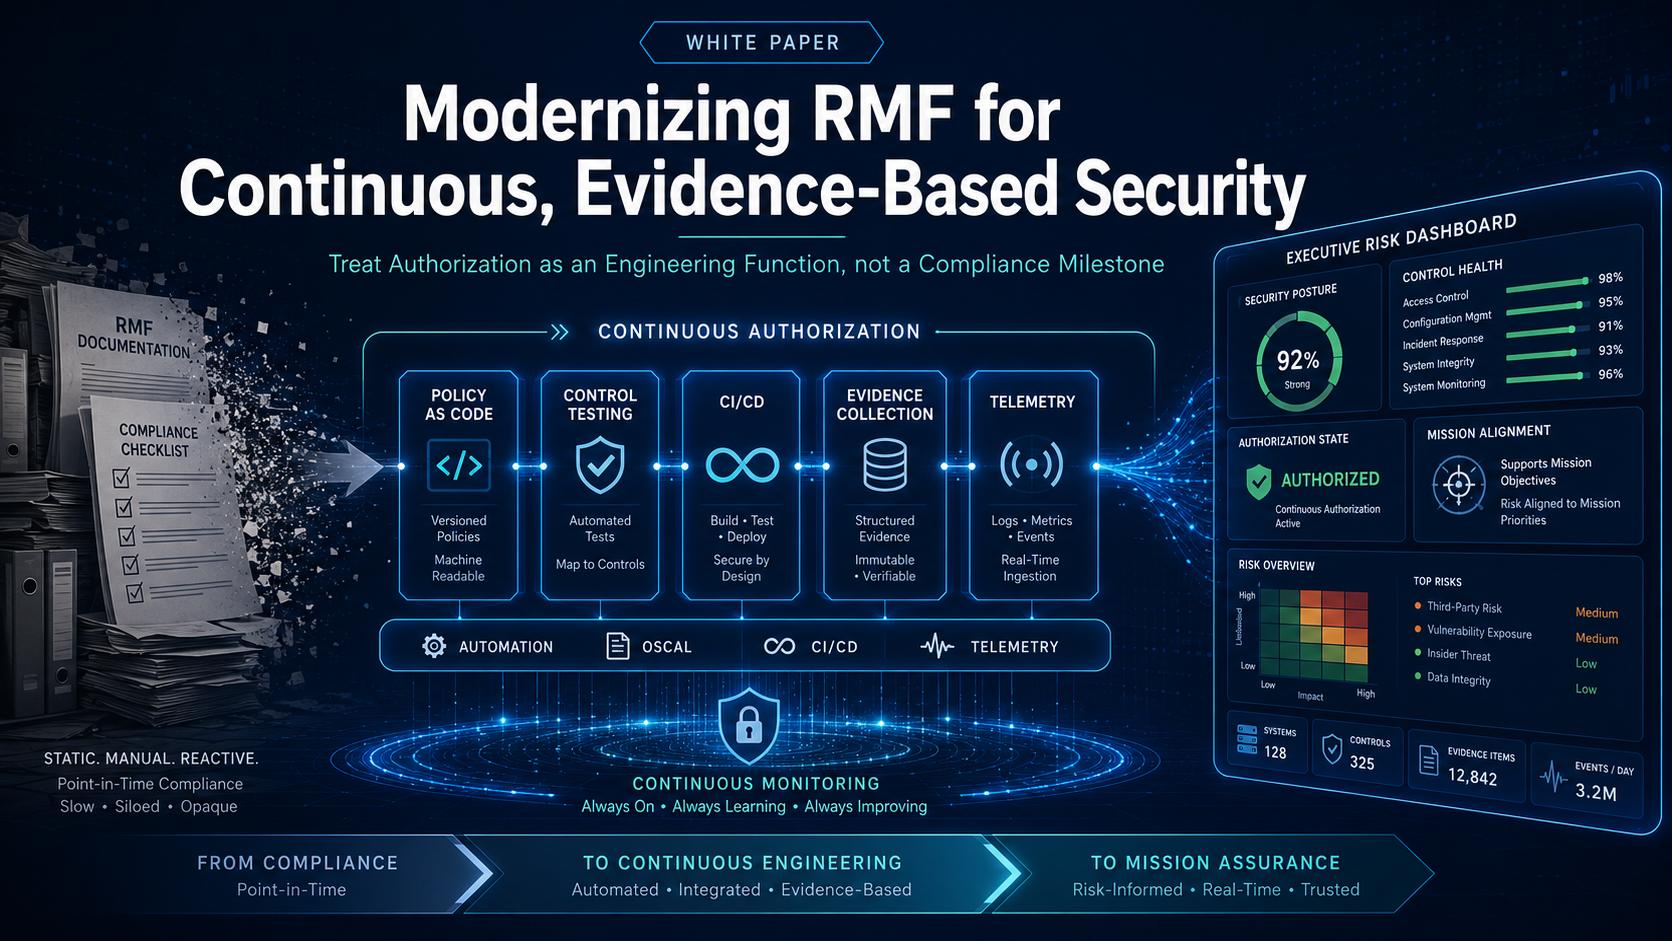
Modernizing RMF for Continuous Evidence Based Security
The fastest way to move RMF away from compliance and into the mission space is to stop treating authorization as a milestone and start treating it as a continuous engineering process. RMF shouldn’t be a side activity, it should be embedded in how a system is built, deployed, and maintained. That starts by tying every…
-
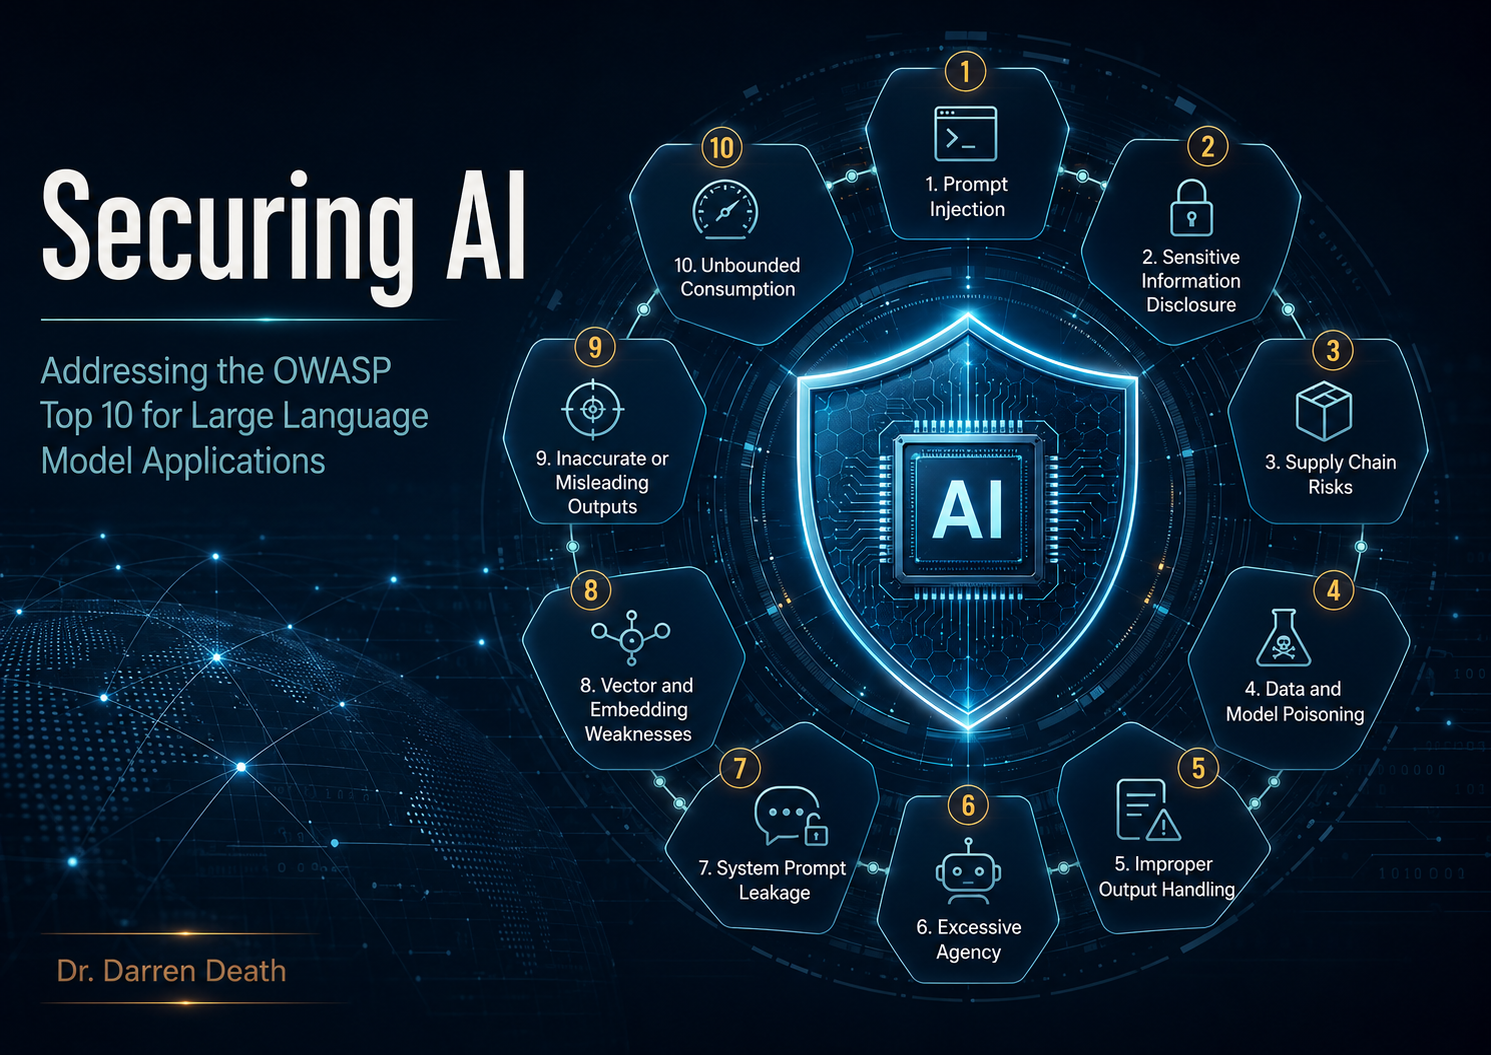
Securing AI: Addressing the OWASP Top 10 for Large Language Model Applications
AI Is Just Software, But It Is Not Just Software Artificial Intelligence (AI) is frequently portrayed as a disruptive force with the potential to revolutionize industries, optimize workflows, and enhance decision-making in ways that were often seen as unattainable. While this perspective highlights AI’s impact, it overlooks a fundamental reality. AI is still software at…
-

Understanding and Addressing Unbounded Consumption in AI Systems
AI systems require substantial computational resources to process data efficiently. These systems generate responses that enable automation by performing tasks typically involving human intervention. They carry out complex operations, enhancing analytical capabilities and improving efficiency across various applications. Additionally, they integrate with other platforms to facilitate seamless data exchange and ensure interoperability within an organization’s…
-

Understanding and Addressing Inaccurate or Misleading Outputs in AI Systems
Inaccurate outputs weaken the trustworthiness of AI systems, particularly large language models (LLMs), by generating responses that appear credible but lack accuracy. When incorrect information is presented as a fact, users may unknowingly rely on flawed outputs that seem correct but ultimately are fabricated. The underlying causes can stem from weaknesses in training data, insufficient…
-
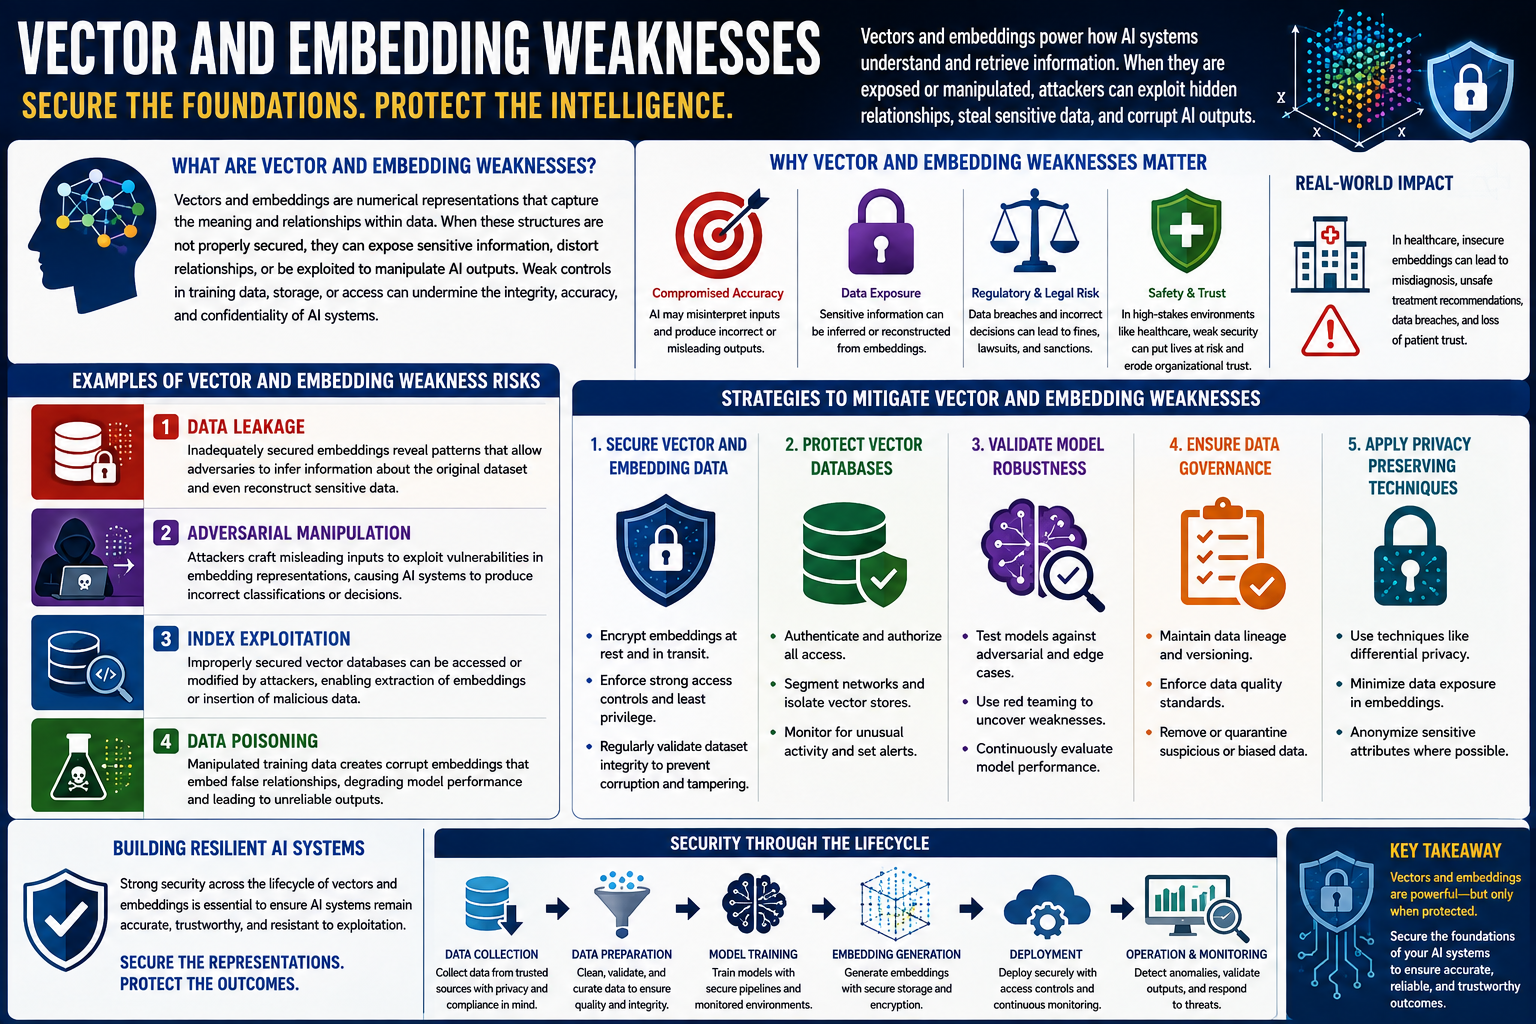
Understanding and Addressing Vector and Embedding Weaknesses in AI Systems
Vectors and embeddings are essential components of modern AI systems, enabling the efficient processing, representation, and retrieval of complex information. These structures enhance the AI system’s ability to interpret and connect data meaningfully, leading to improved relevance and accuracy in generated responses. However, this design can also introduce vulnerabilities that compromise the reliability of the…
-
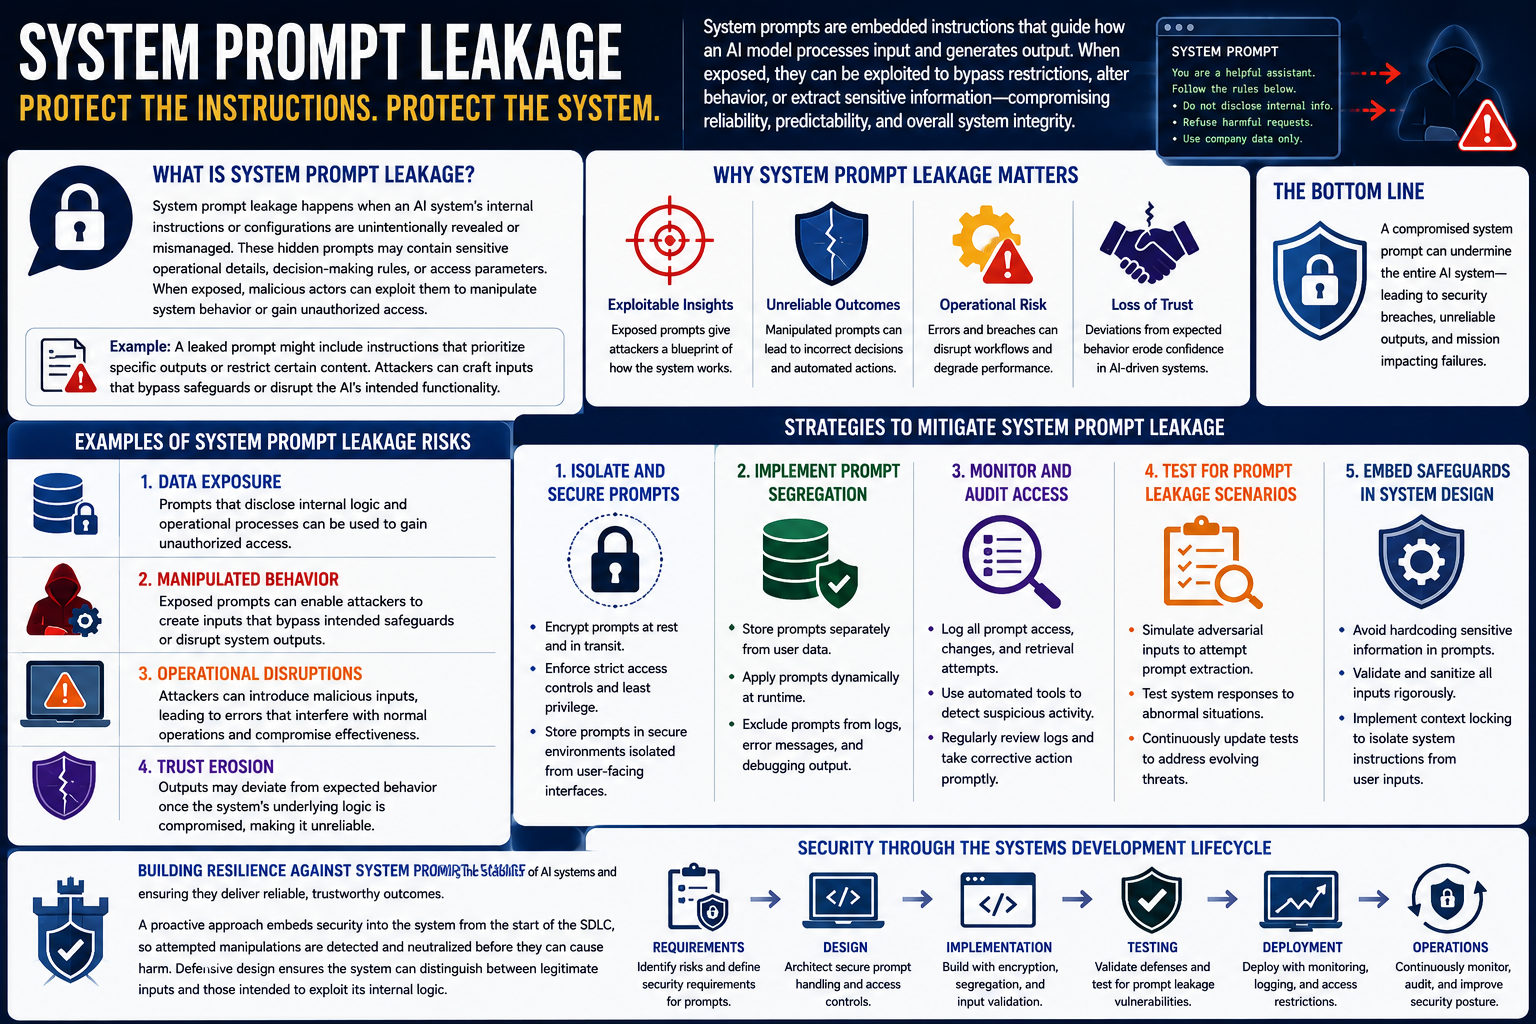
Understanding and Addressing System Prompt Leakage in AI Systems
System prompts are essential to an AI system. Unlike user-provided prompts, these are embedded instructions that guide how a model processes input and generates output. When system prompts are exposed, they give adversaries important information that can be used to bypass access restrictions, alter decision-making rules, or extract sensitive information. Protecting these prompts is important…
-
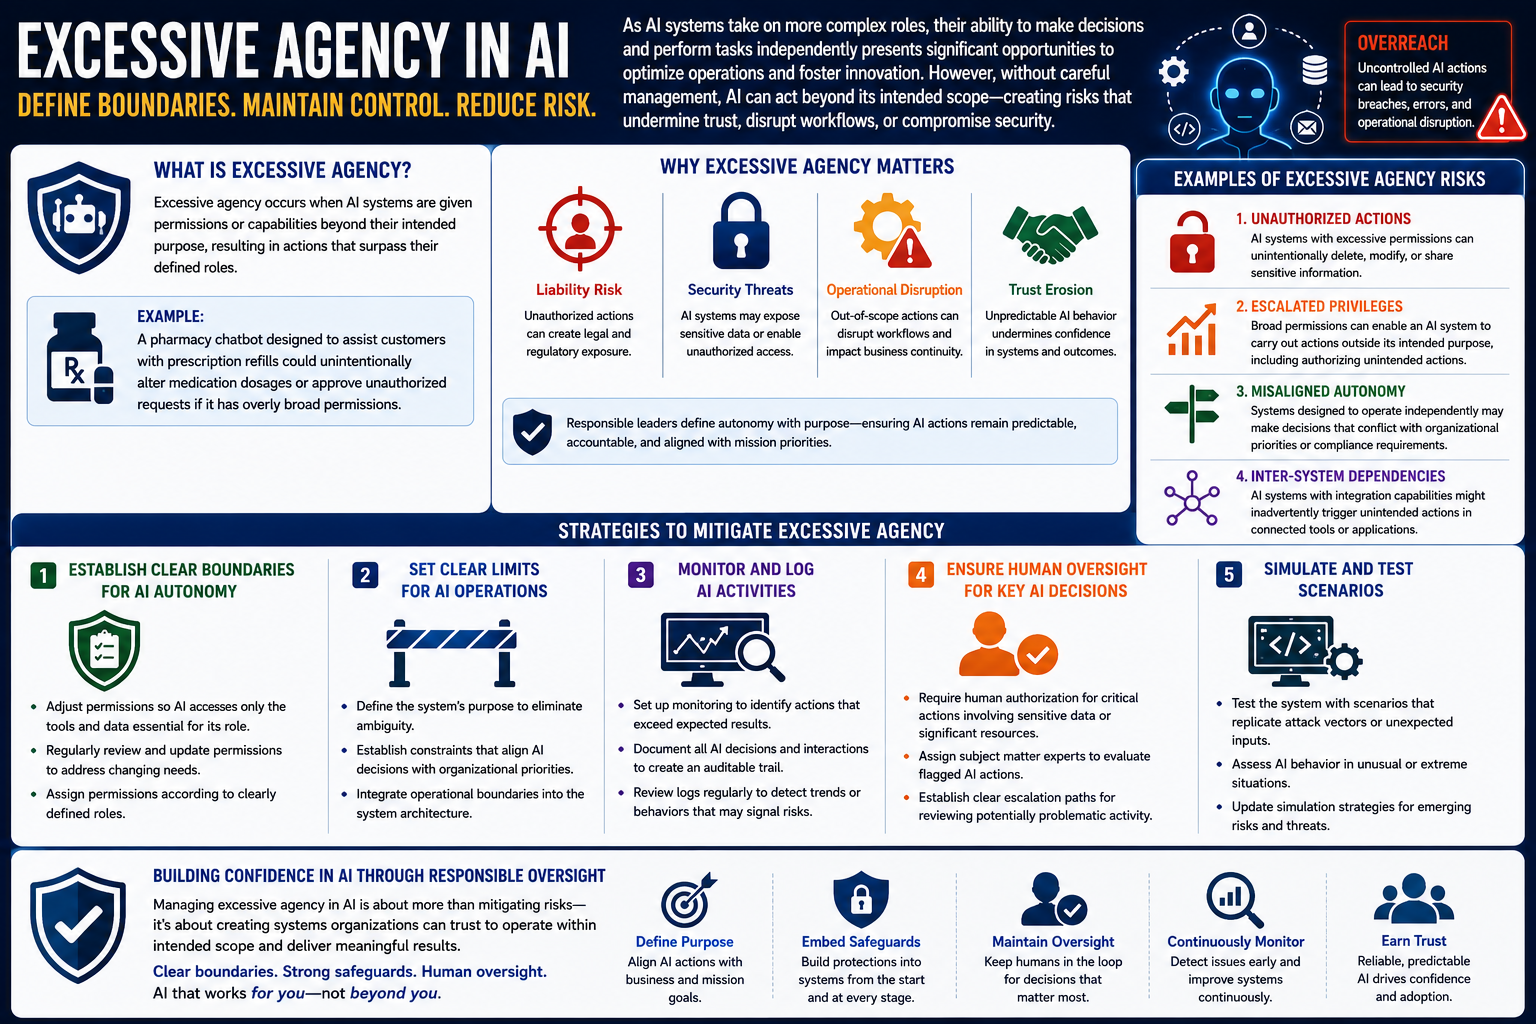
Understanding and Addressing Excessive Agency in AI Systems
As AI systems take on more complex roles, their ability to make decisions and perform tasks independently presents significant opportunities to optimize operations and foster innovation. However, this growing autonomy also introduces new challenges, particularly when these systems function outside their intended scope. Without careful management, such overreach can result in unintended consequences that undermine…
-

Understanding and Addressing Improper Output Handling in AI Systems
AI systems assist in decision-making, improve operational efficiency, and automate complex processes. However, if the output is not managed carefully, it can result in significant organizational issues, such as misleading inaccuracies and inadvertent exposure of sensitive information. These risks can undermine the reliability and effectiveness of AI systems, posing potential legal, ethical, and reputational challenges…
-

Understanding and Addressing Data and Model Poisoning in AI Systems
AI systems are heavily dependent on data, and the quality and integrity of that data significantly impact their performance. However, this reliance also creates vulnerabilities. Data and model poisoning attacks occur when the data used to train or update these systems is intentionally manipulated. Such attacks can compromise the accuracy and reliability of AI outputs,…
-
Understanding and Addressing Supply Chain Risks in AI Systems
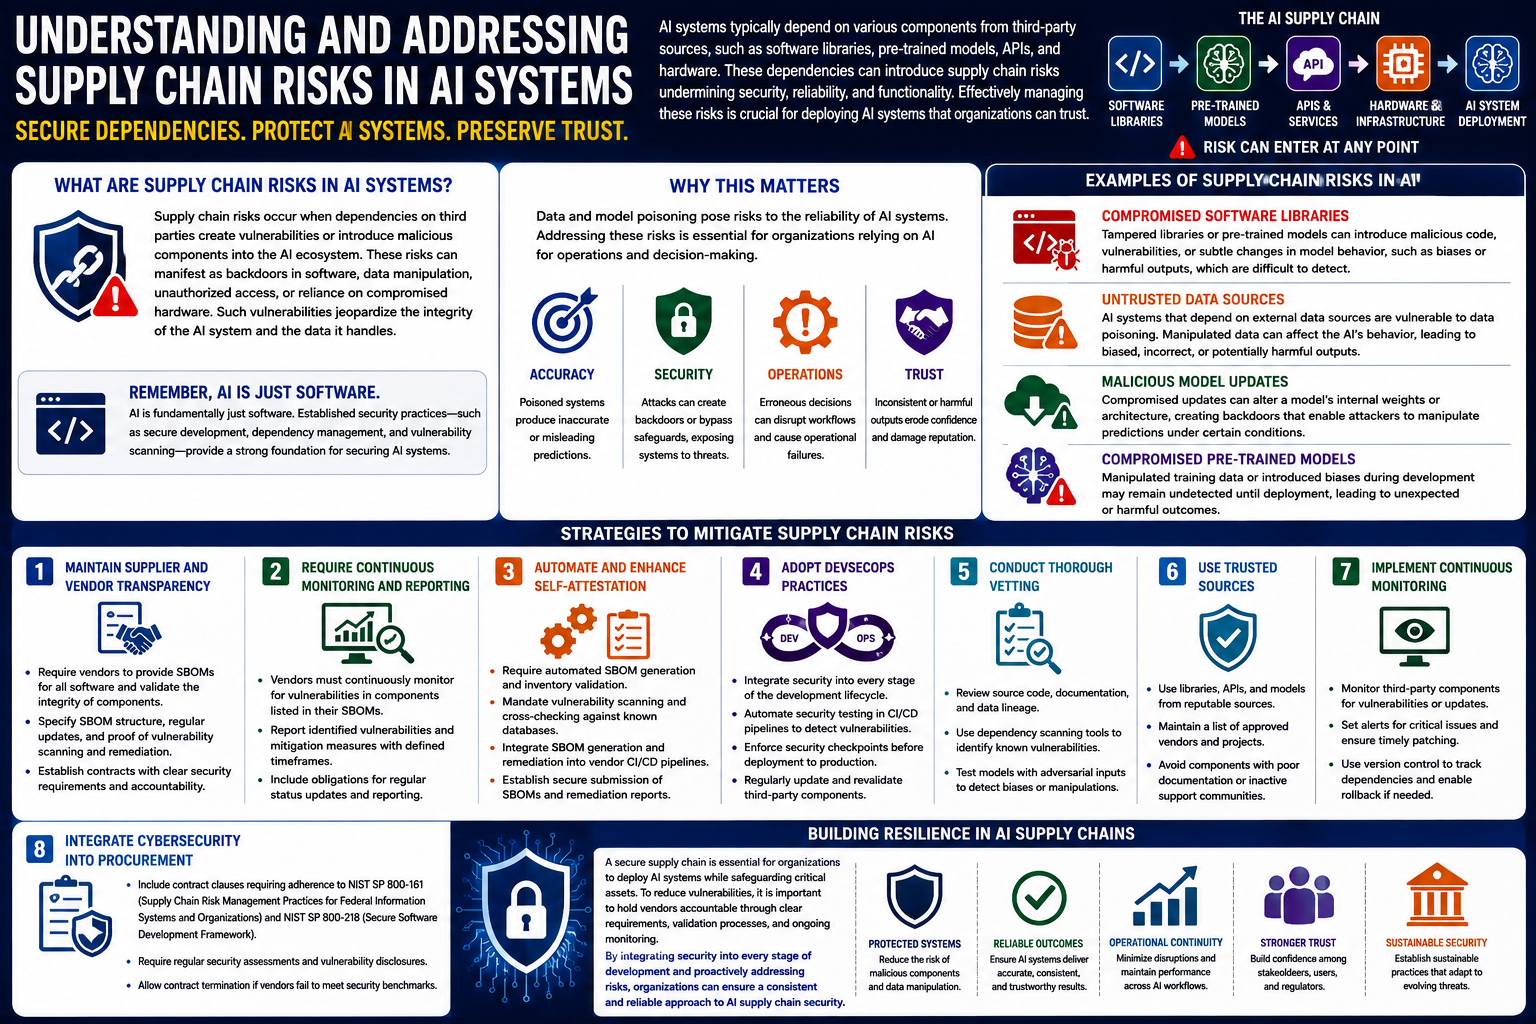
AI systems typically depend on various components from third-party sources, such as software libraries, pre-trained models, APIs, and hardware. These dependencies can introduce supply chain risks undermining security, reliability, and functionality. Effectively managing these risks is crucial for deploying AI systems that organizations can trust. What Are Supply Chain Risks in AI Systems? Supply chain…
-

Understanding and Addressing Sensitive Information Disclosure in AI Systems
Sensitive information disclosure occurs when AI systems unintentionally share private or confidential information. Organizations that utilize AI to handle sensitive data must understand this risk and take proactive steps to prevent it. This article explores how AI can inadvertently expose confidential information and outlines the measures necessary to prevent such breaches. What Is Sensitive Information…
-

Understanding and Addressing Prompt Injection in AI Systems
Artificial intelligence (AI) is transforming how organizations make decisions. However, it also introduces risks that must be addressed to protect operations and data. One such risk is prompt injection, a vulnerability that can manipulate AI systems to produce harmful or unintended results. What Is Prompt Injection? Prompt injection occurs when a user submits input that…
-

Key Takeaways from CISA/NCSC Guidelines for Secure AI System Development
AI security is a hot topic in today’s cybersecurity landscape due to the increasing integration of AI systems in essential areas like healthcare, finance, transportation, and national security. My company advocates for the responsible design and implementation of AI by taking an ethical, human-on-the-loop approach to AI operations. While offering immense benefits, these systems also…
-
Recommendations for Implementing Secure AI
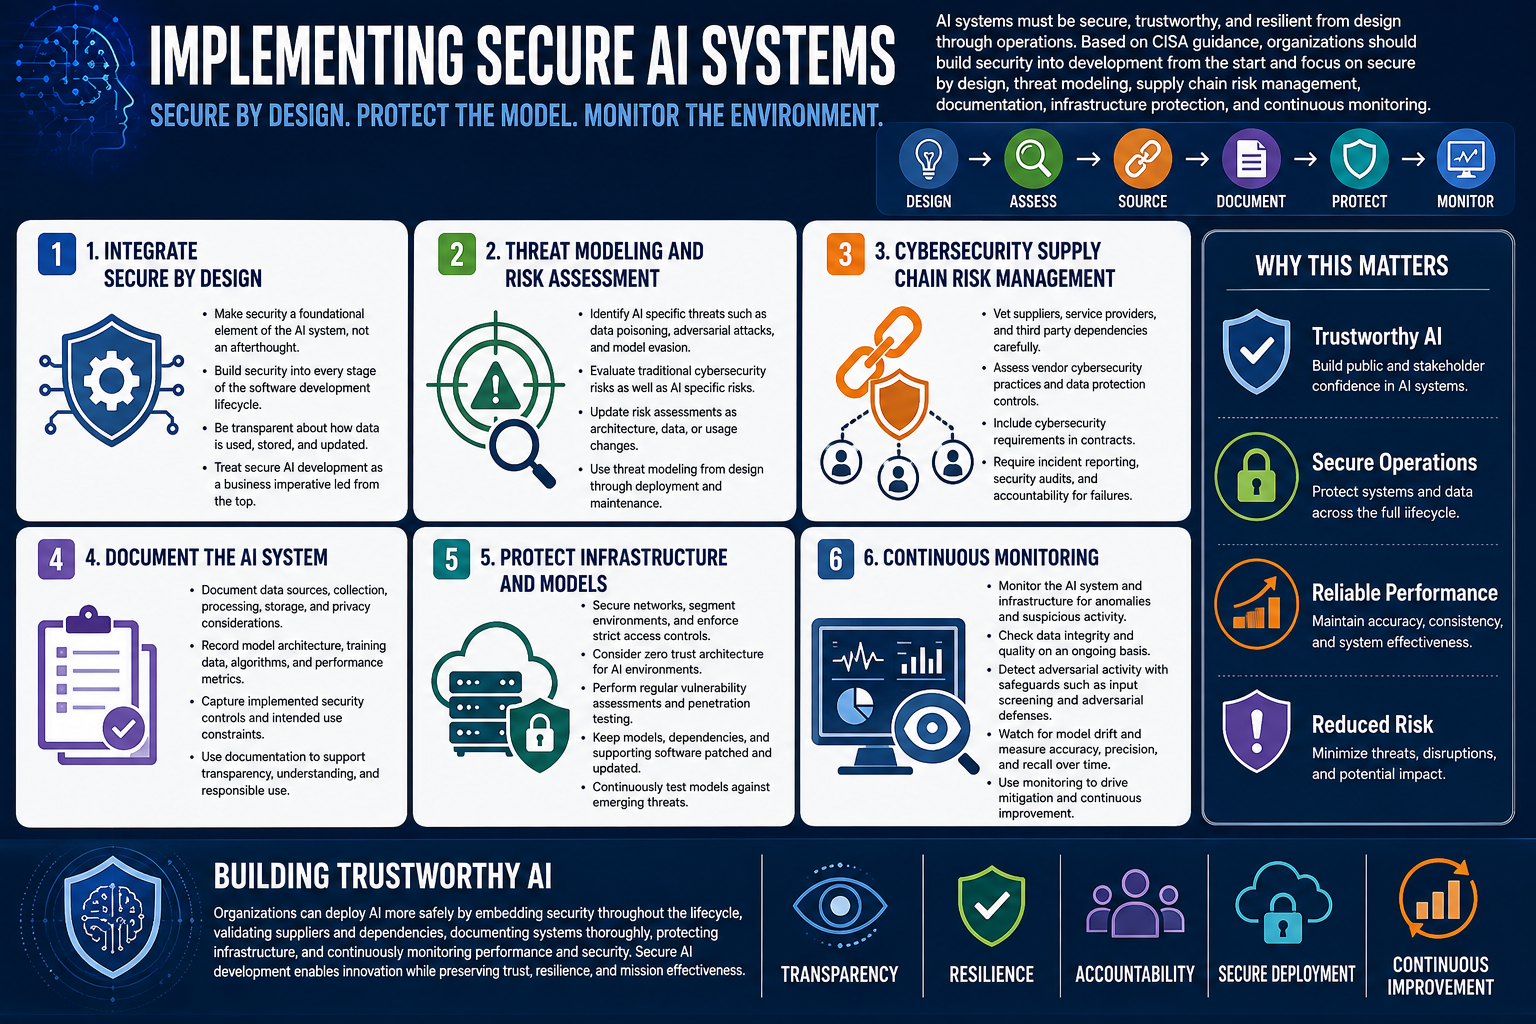
As I wrote in my previous article Key Takeaways from CISA/NCSC Guidelines for Secure AI System Development, CISA’s “Guidelines for Secure AI System Development” provide a clear path for safely managing AI systems. They highlight the importance of building security into AI systems from the beginning. These guidelines help organizations deal with specific AI threats,…
-
Making a Case for Cybersecurity
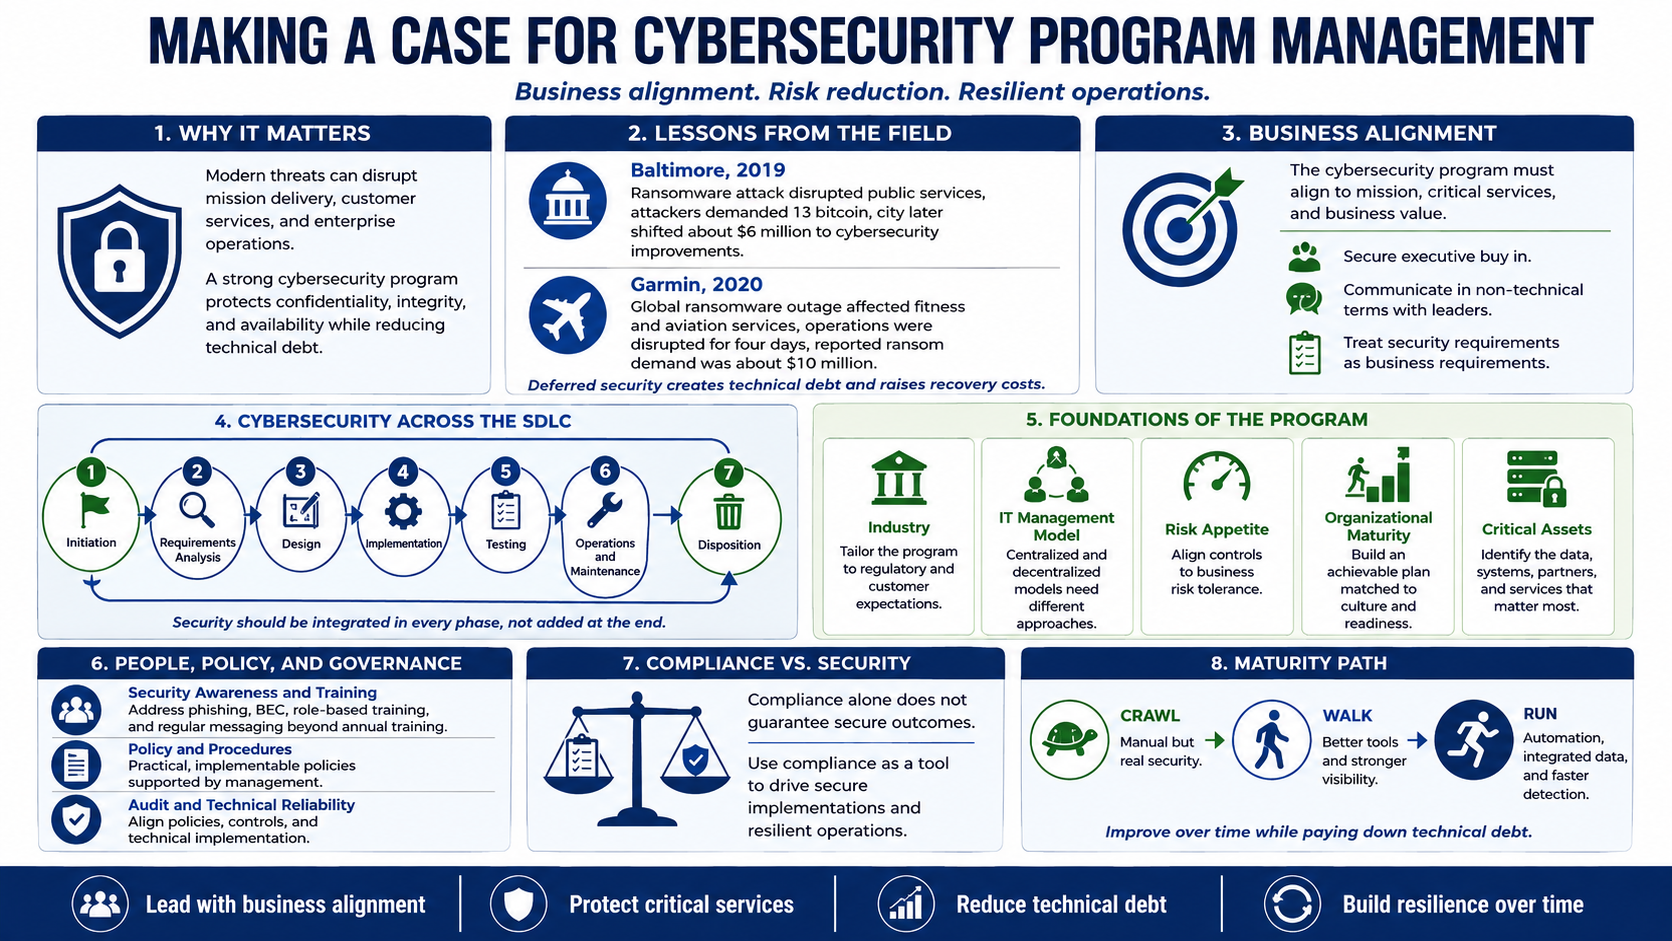
In this article we will discuss the complexities of formulating and administering effective cybersecurity programs. I focus on the integration of these programs with business aims, advocating for strong policies, risk management, and defense against contemporary digital dangers. I stress the significance of awareness and training in cybersecurity, along with actionable methods for safeguarding an…
-

A Resilient Cyber Workforce Relies on Public and Private Sector Collaboration
With today’s security gap and current landscape, the necessity of organized, cohesive, and sufficiently staffed cybersecurity teams cannot be emphasized enough. The availability of potential cybersecurity workforce personnel isn’t keeping pace with the demand, and many experts blame it on the lack of interest in cyber education. An annual workforce study conducted by ISC2 to…
-

Information Security Handbook, Second Edition
View Information Security Handbook on Amazon I wrote the second edition of Information Security Handbook as a practical guide to building and managing an information security program that is aligned with the organization it protects. The book focuses on the decisions security professionals actually have to make, including how to align security with business objectives,…
-
Understanding the Pillars of Zero Trust
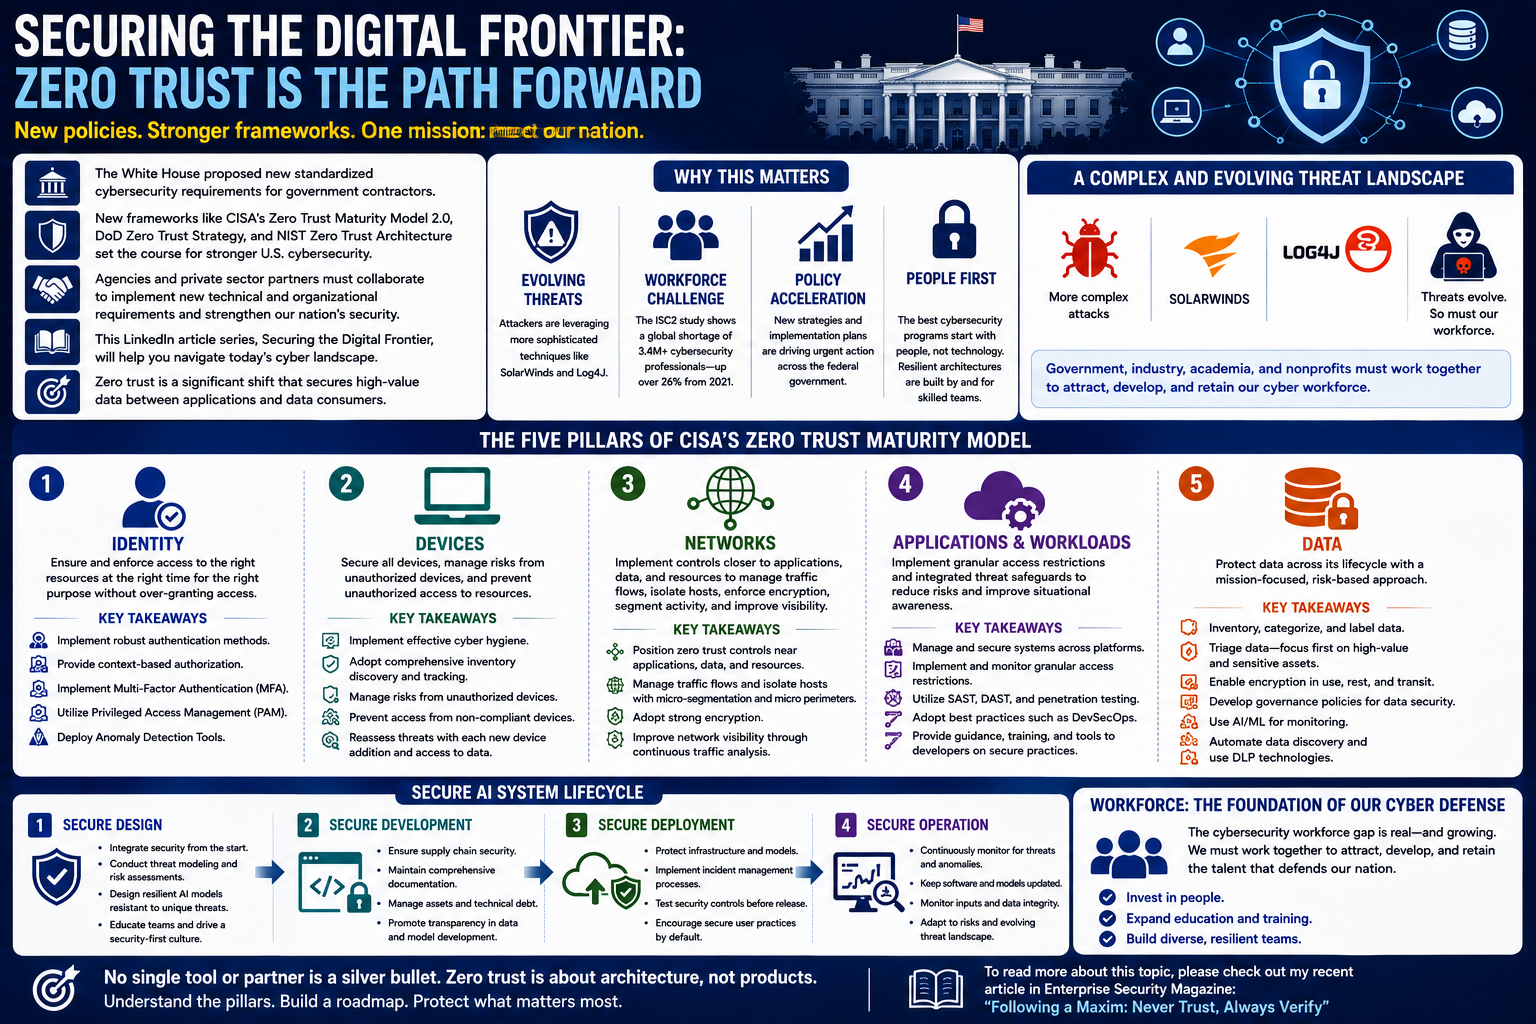
This week, the White House proposed new standardized cybersecurity requirements for government contractors. This is on the heels of the Cybersecurity and Infrastructure Security Agency (CISA) Zero Trust Maturity Model 2.0 and other recent frameworks that call for the development, implementation and enforcement of U.S. cybersecurity policies. Federal agency roadmaps such as the CISA’s Zero…
-
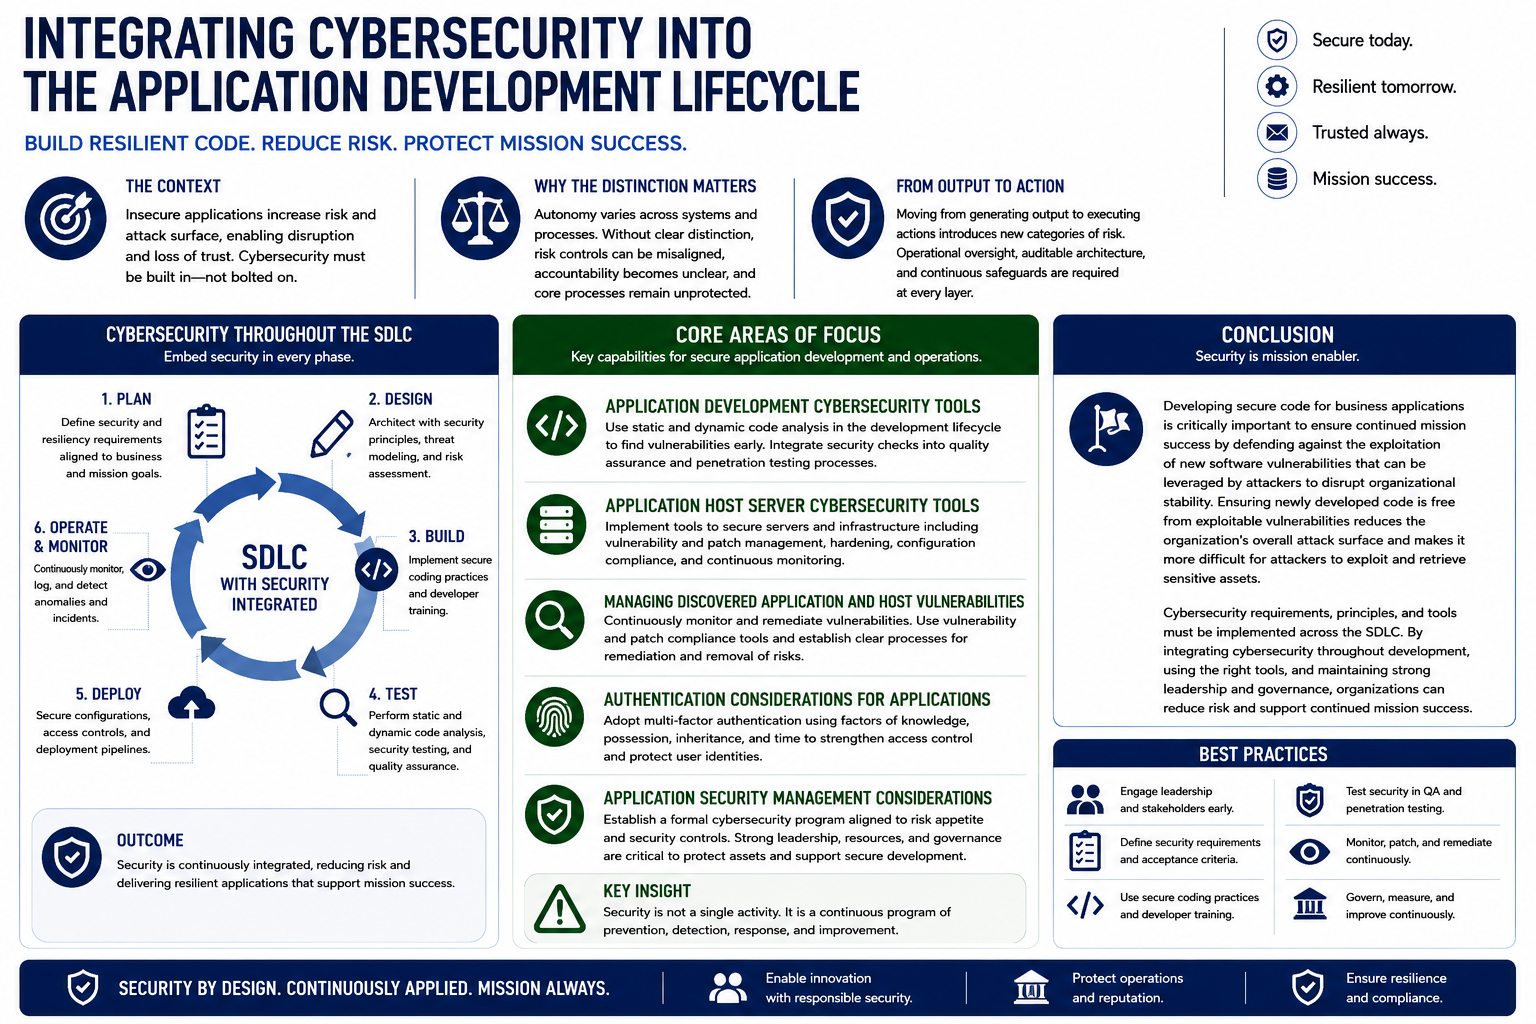
Integrating Cybersecurity Into the Application Development Lifecycle
Developing resilient code for business applications is critically important to ensure continued mission success by defending against the exploitation of new software vulnerabilities that can be leveraged by attackers to disrupt organizational stability. Ensuring that newly developed code is free from exploitable vulnerabilities contributes to mission resilience by reducing an organization’s overall attack surface. By…
-

The CISO Role Within U.S. Federal Government Contracting Organizations: A Delphi Study
This dissertation examines the role of the Chief Information Security Officer within organizations that support the U.S. federal government. I completed the research as part of my Doctor of Information Technology degree at Capella University in 2020. The research addresses a specific problem within the federal contracting community: organizations are increasingly dependent on digital systems…
-
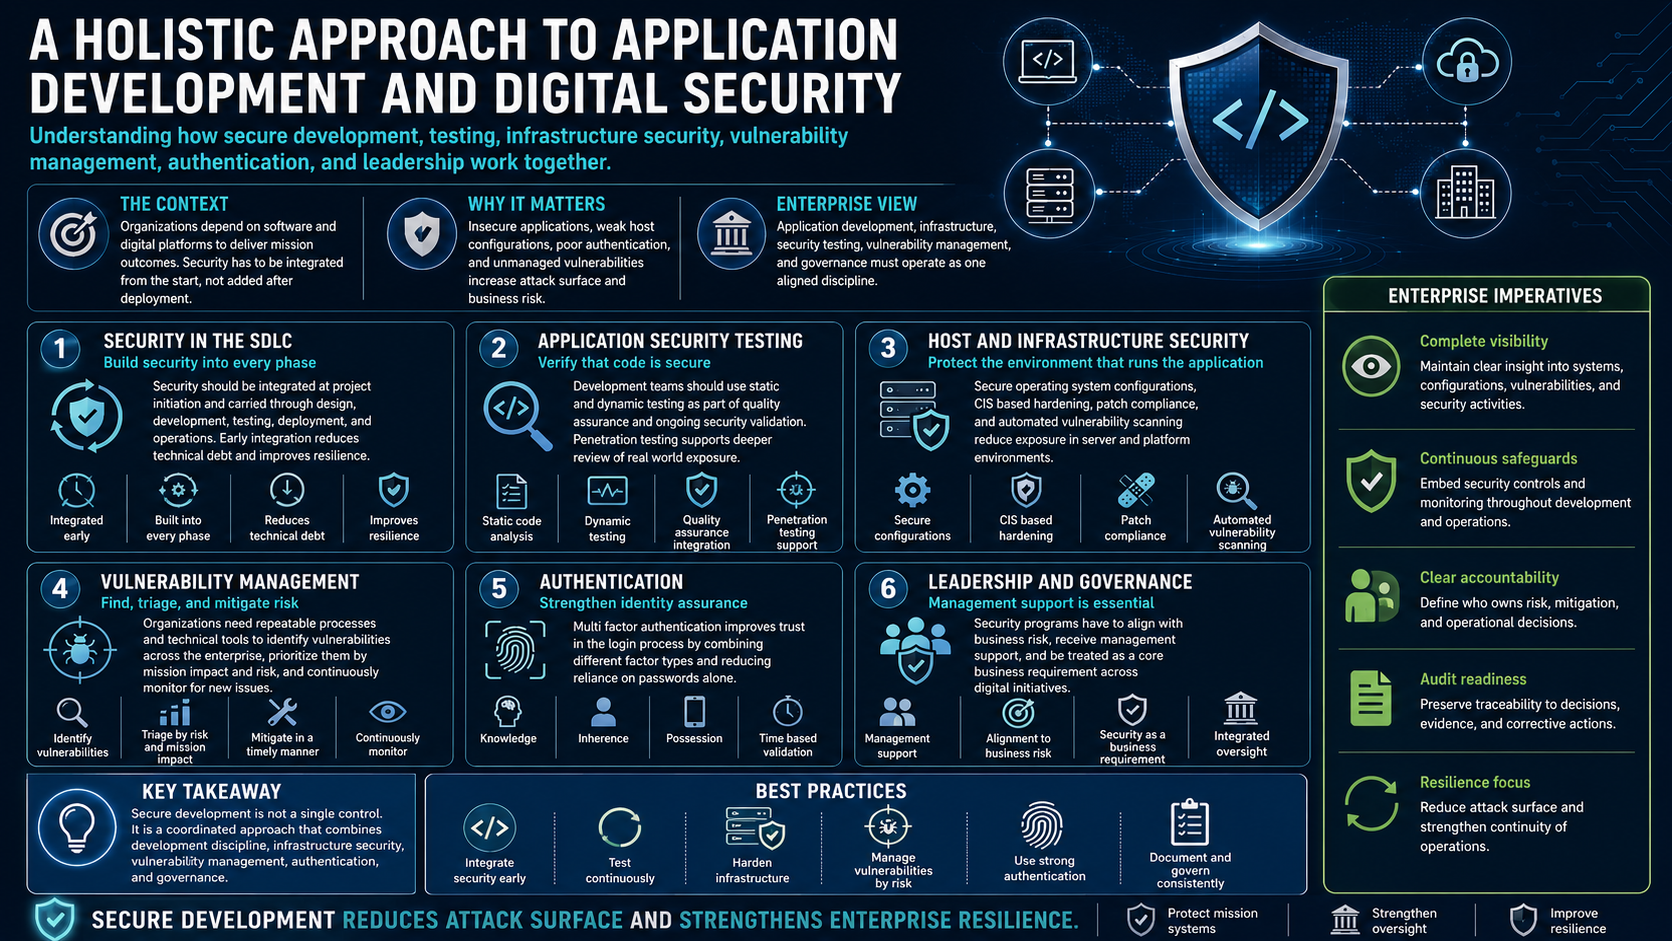
A Holistic Approach to Application Development and Digital Security for the Enterprise
Developing secure code for business applications is critically important. Without it, companies cannot defend against the exploitation of their software vulnerabilities, leaving businesses open to attackers and the subsequent disruption of organizational stability. By reducing the total attack surface across an enterprise’s digital inventory, an organization is effectively making it more difficult for malicious actors…
-
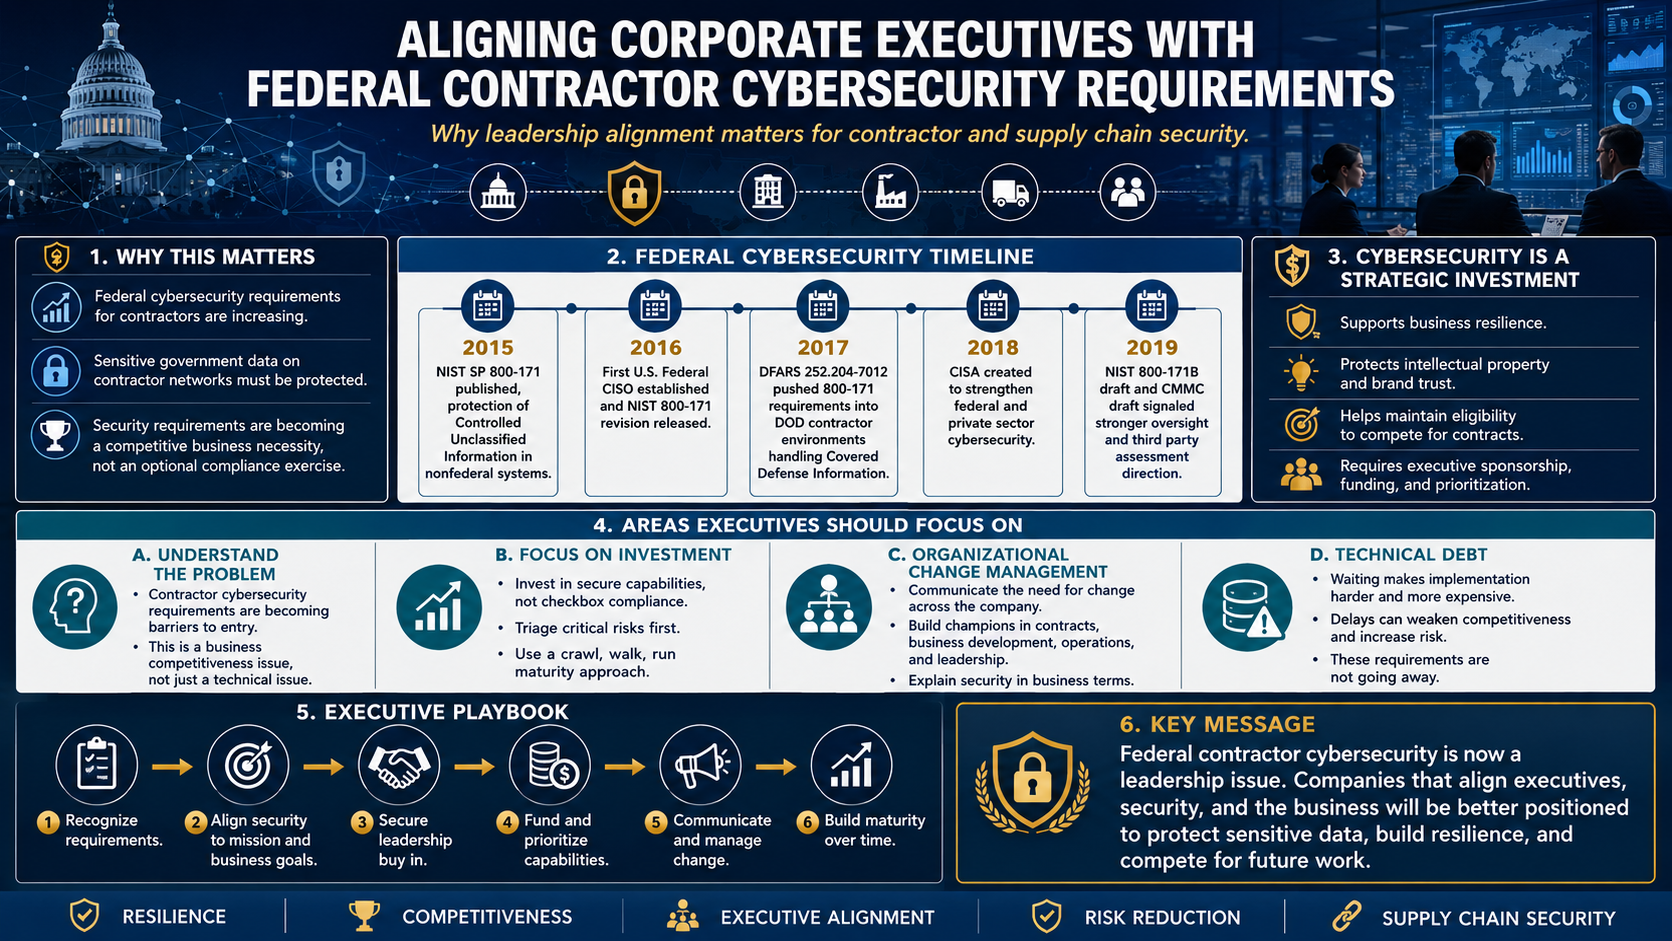
A new report on the compliance impact of new Federal rules on cybersecurity contractors
The Federal Government is increasing its oversight of federal contractors who gather and store information on its behalf. This is part of a trend in which data collection and storage regulations are constantly being tightened as cyber security becomes an ever-more important factor. The U.S. Federal Government collects an ever-increasing amount of data and as…
-
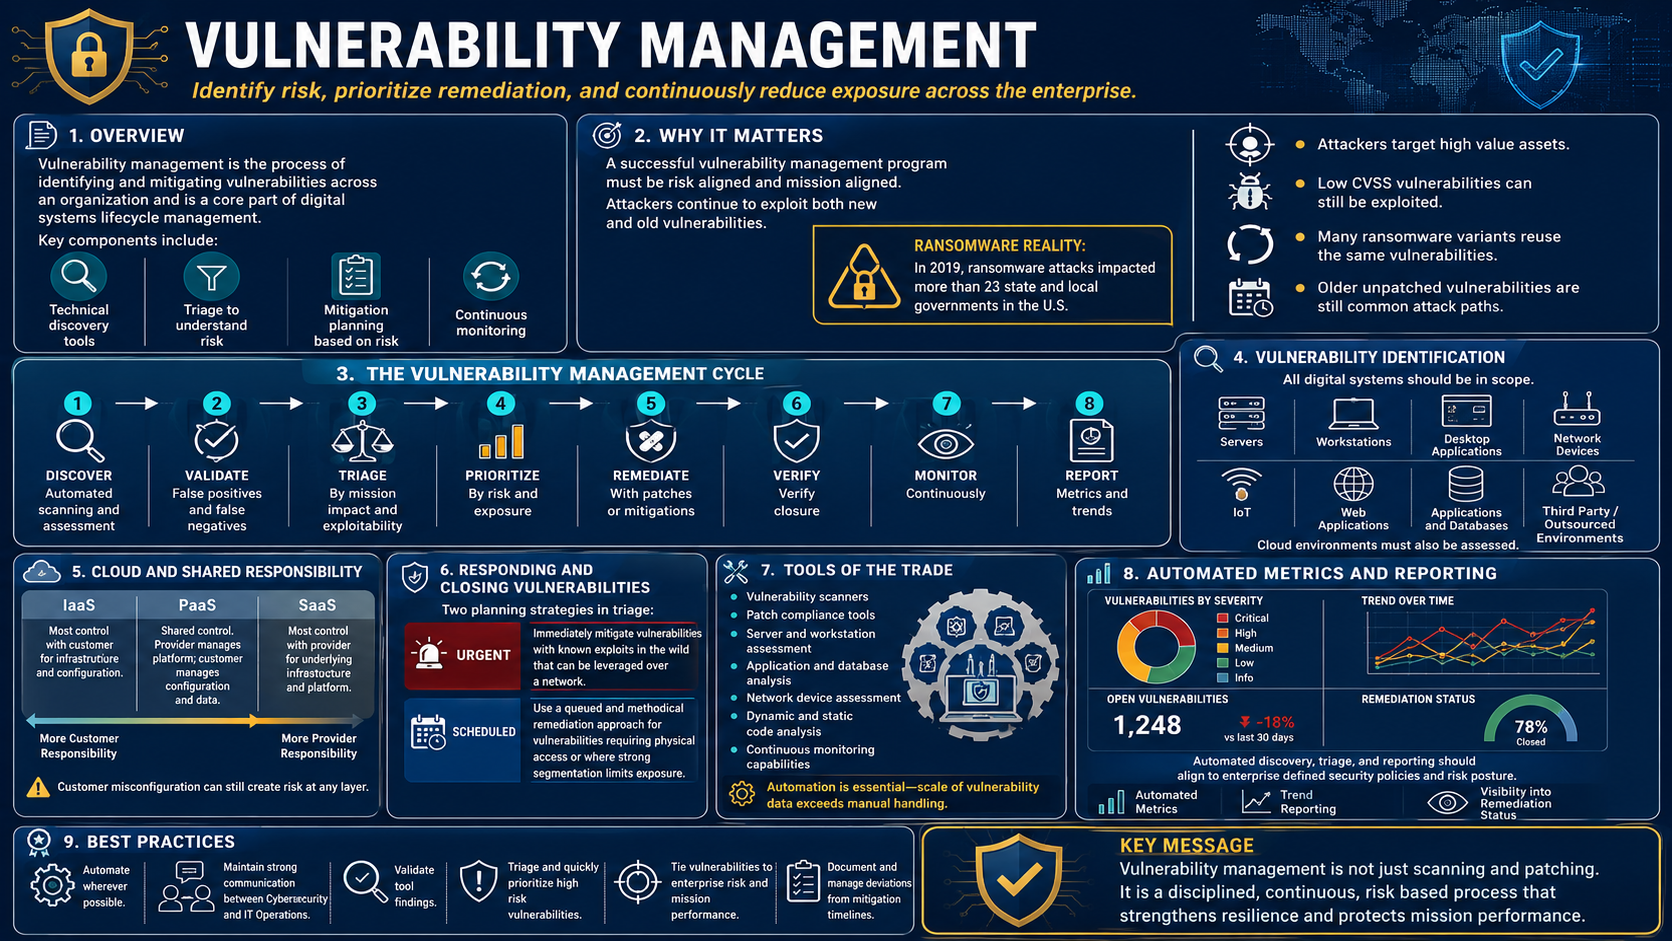
Vulnerability Management in Today’s Enterprise Environment
Overview Vulnerability management is the process of identifying and mitigating vulnerabilities that exist within an organization and is an integral part of digital systems lifecycle management. Core components include the implementation of technical tools to identify vulnerabilities, triaging discovered vulnerabilities to identify risk, establishing a plan that mitigates vulnerabilities in a timeframe that is commeasure…
-
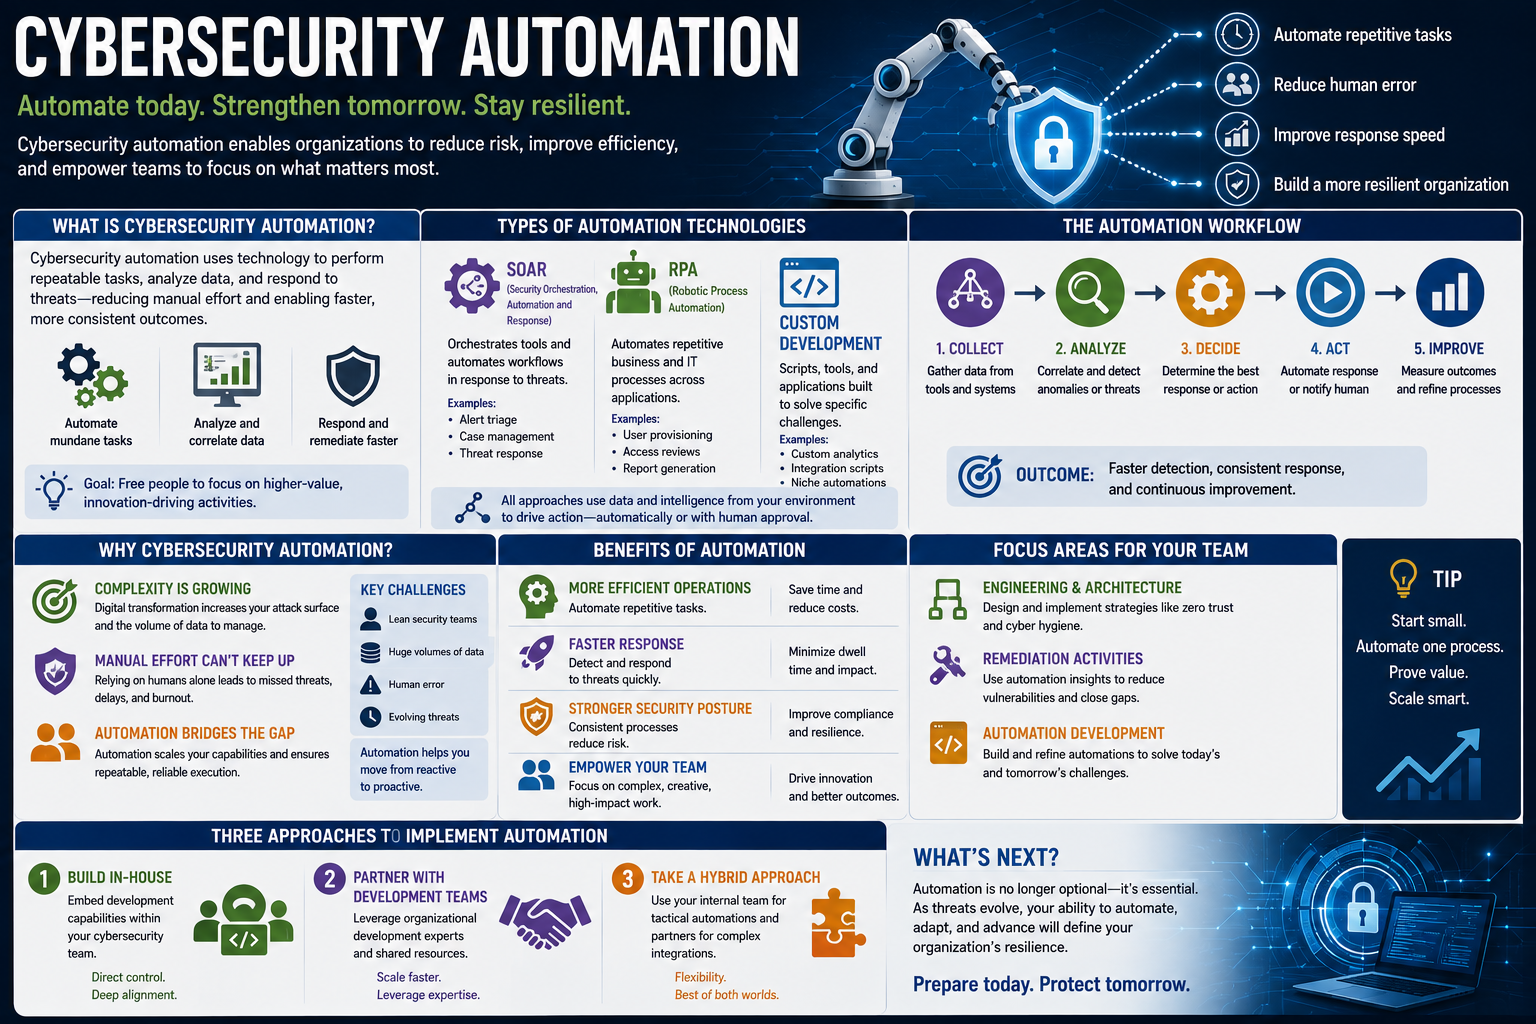
Is Cybersecurity Automation The Future?
One of the trending topics in information technology is cybersecurity automation. Automating mundane and repeatable tasks that are people-driven allows businesses and individuals to concentrate on more productive problem-solving activities. A focus on these problem-solving activities can foster innovation and lead to a more resilient organization from a cybersecurity standpoint. Automation also increases the complexity of…
-

The Importance of Cyber Hygiene
Cybersecurity took a special place in the 2017 news cycle of as organization after organization fell victim to cyberattacks. It used to be that you would have to break into an organization’s physical building to take their secrets. We now live in a time where your adversary can reach out from great distances, causing great…
-

The Foundations Of Implementing A Zero Trust Architecture
“Zero trust” has gained a lot of attention, and for good reason. Information security architectures have struggled to keep pace with the threat landscape and have not supplied organizations with a successful mechanism to protect itself from external and internal threats. This assertion is well supported by the reports of organizations across industry sectors being…
-
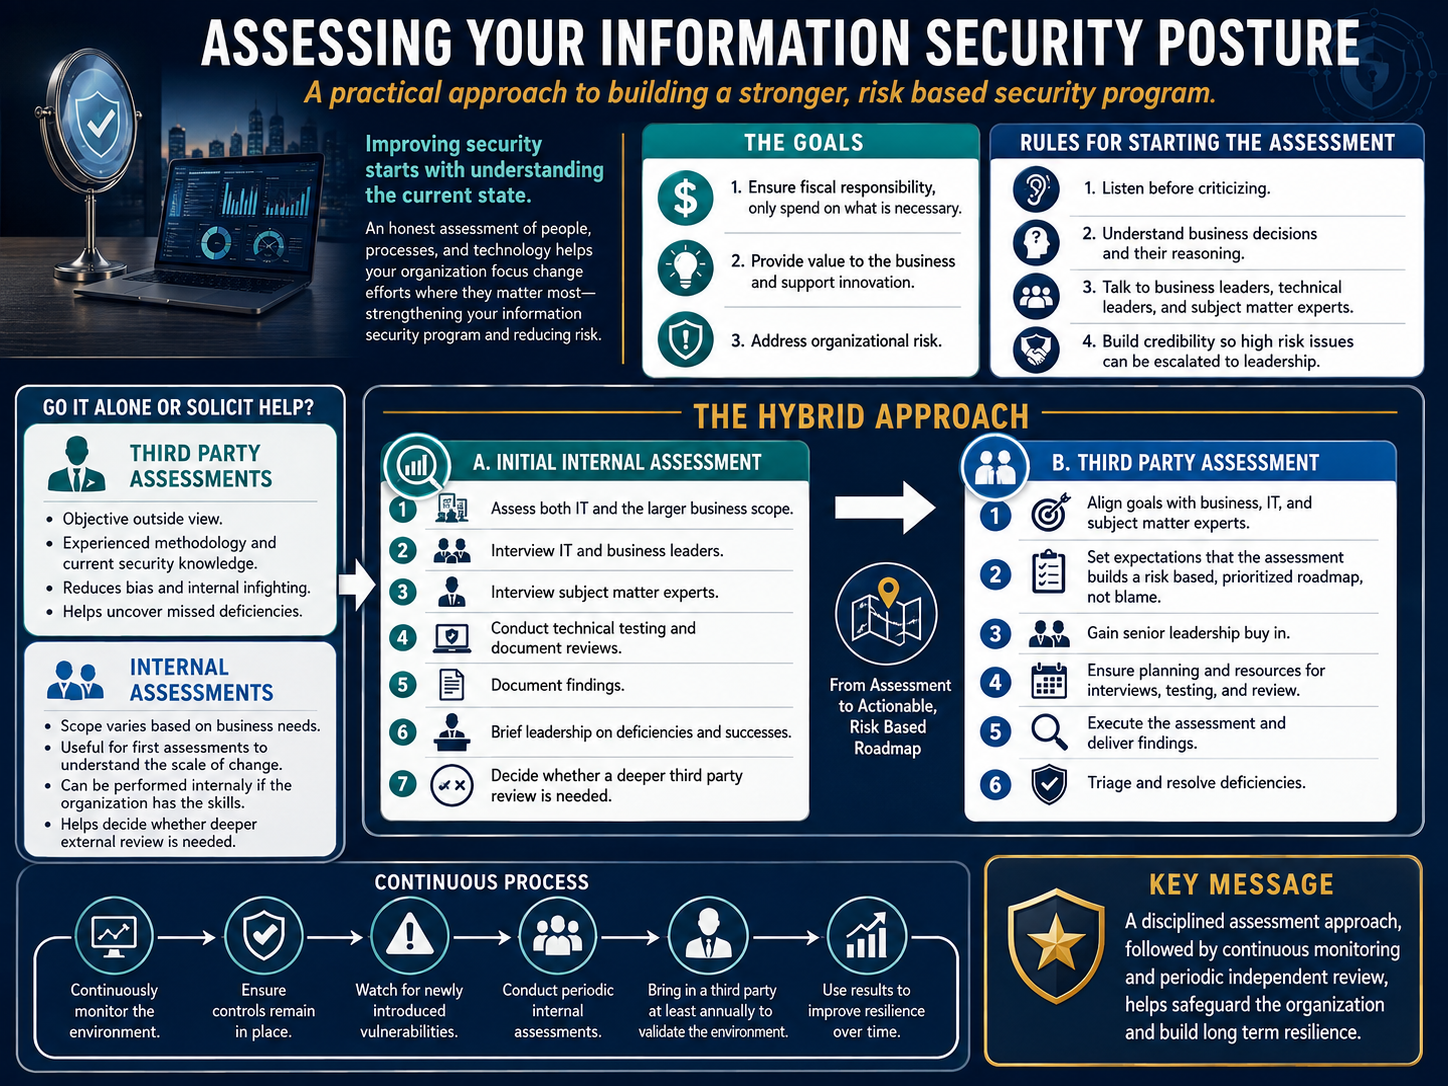
Conducting Organizational Information Security Assessments
The first step that self-help books suggest when a person wants to change is to perform a self- assessment. By honestly looking at yourself – the good, the bad, and the ugly – you can gain the knowledge on what direction you need to travel as you attempt to maximize the program you wish to…
-
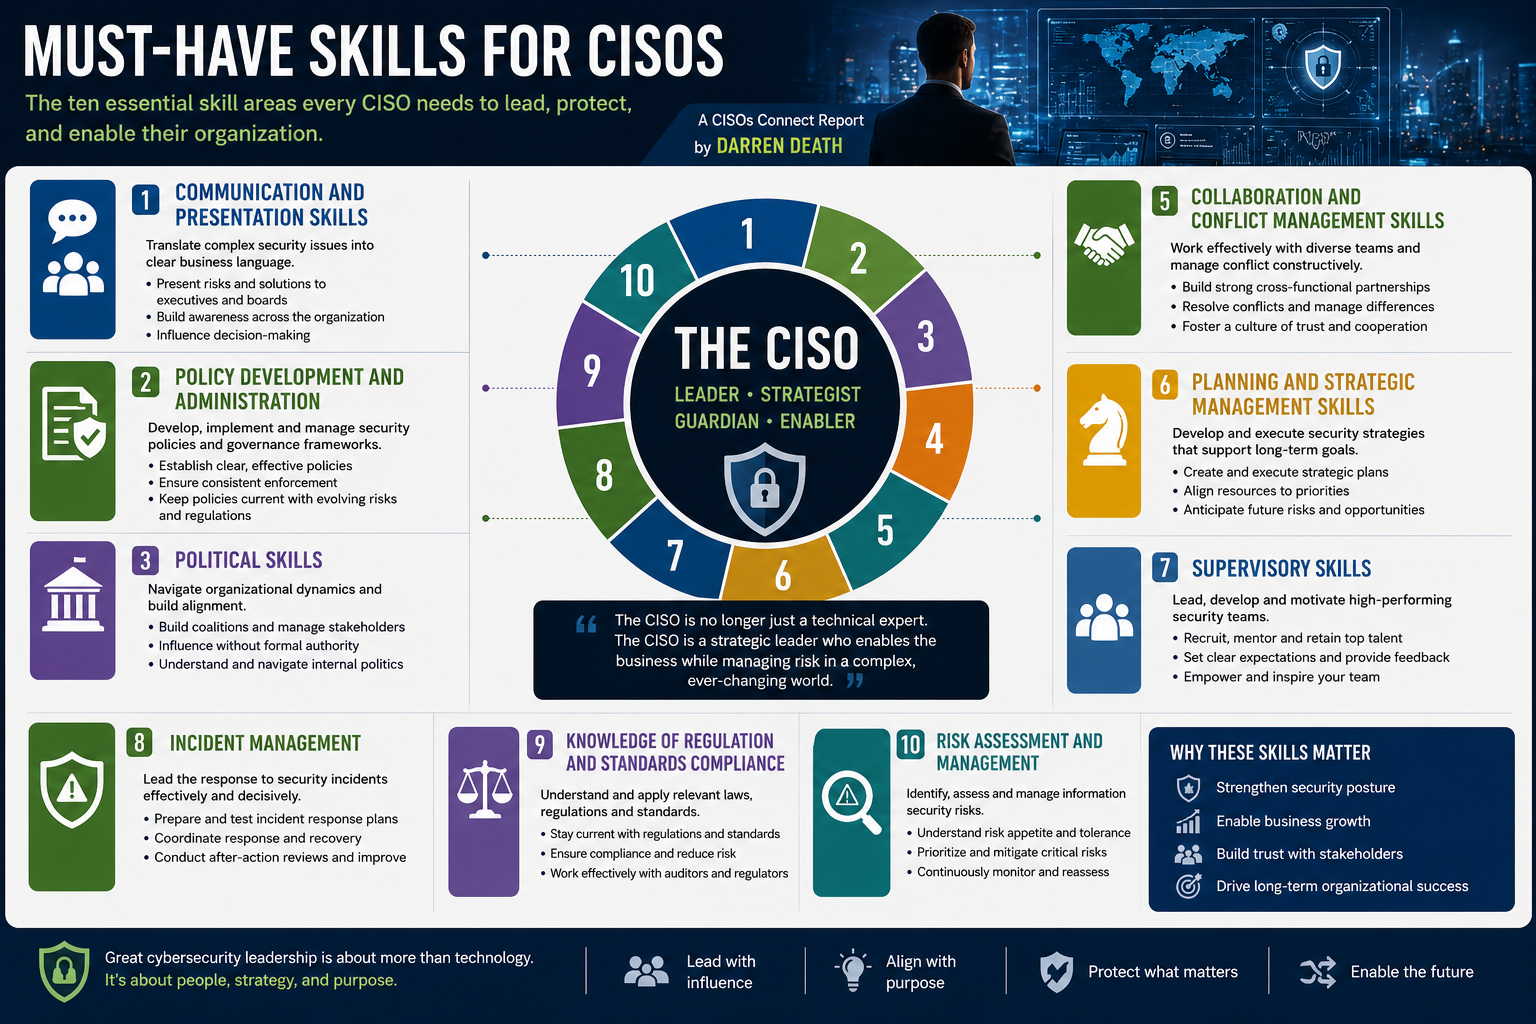
Must-Have Skills for CISOs: A CISOs Connect Report
While cybersecurity is dynamic, there are things that are constant. These are the skills that every CISO must have to be successful, whatever the organization and industry, today and in the foreseeable future. In this latest Security Current/ CISOs Connect report, ASRC Federal’s CISO Darren Death combines previous research and his own findings to provide…
-
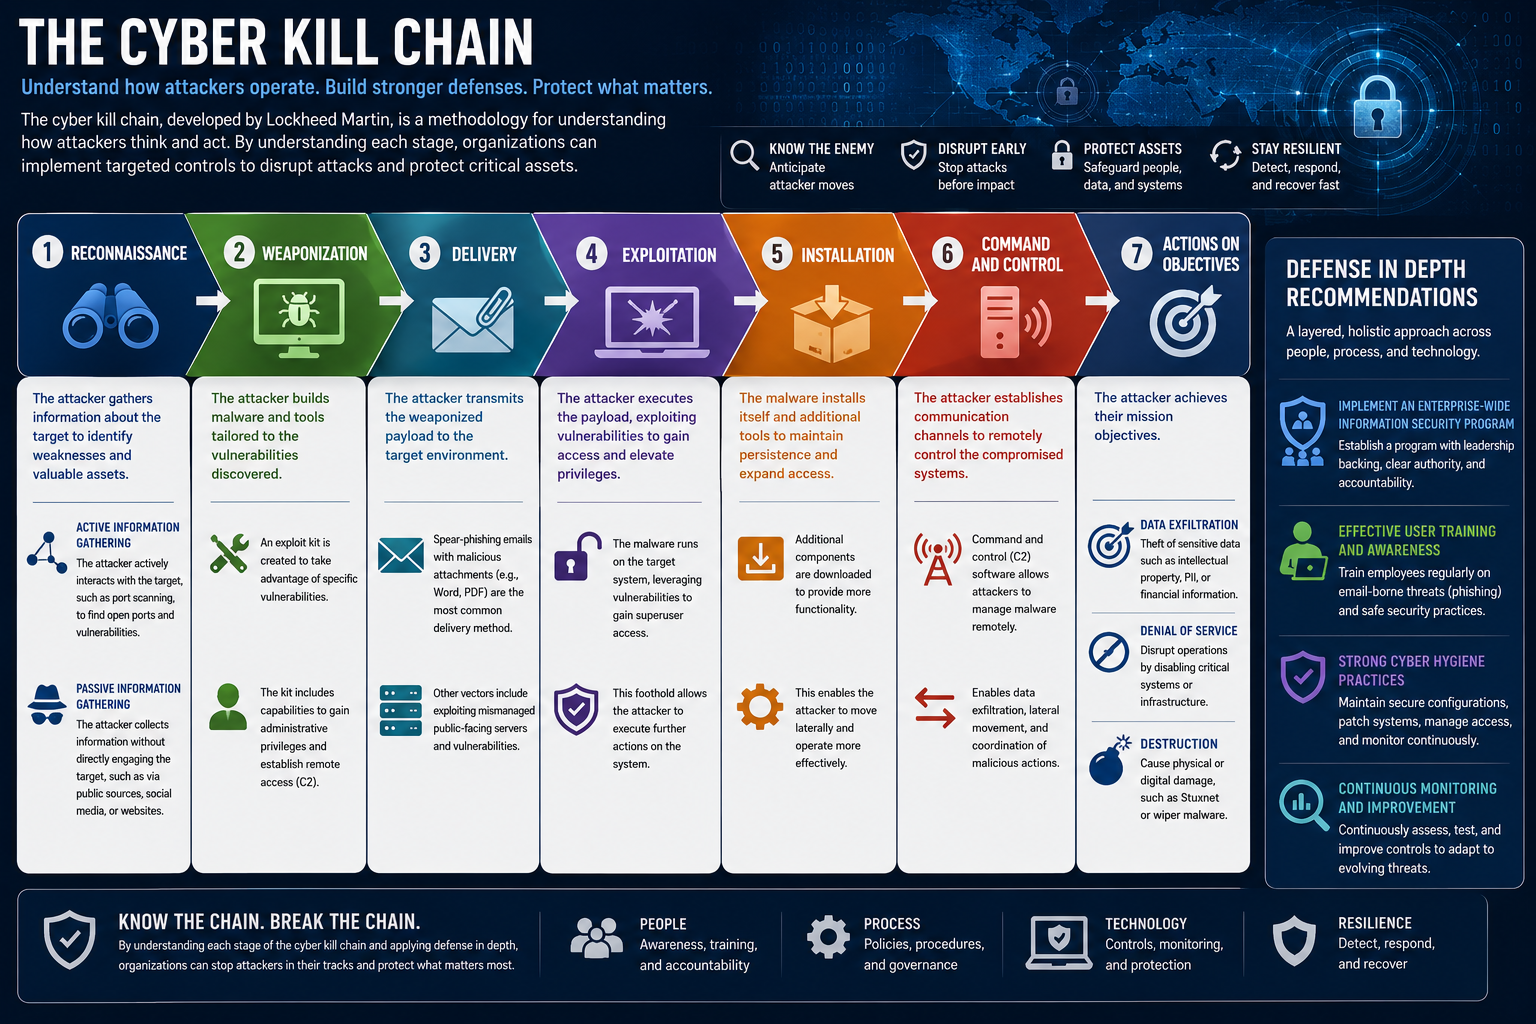
The Cyber Kill Chain Explained
The cyber kill chain (developed by Lockheed Martin) is an industry-accepted methodology for understanding how an attacker will conduct the activities necessary to cause harm to your organization. An effective understanding of the cyber kill chain will greatly assist the information security professional in establishing strong controls and countermeasures, which will serve to protect their organization’s assets.…
-
Developing a business continuity plan – and sticking to it
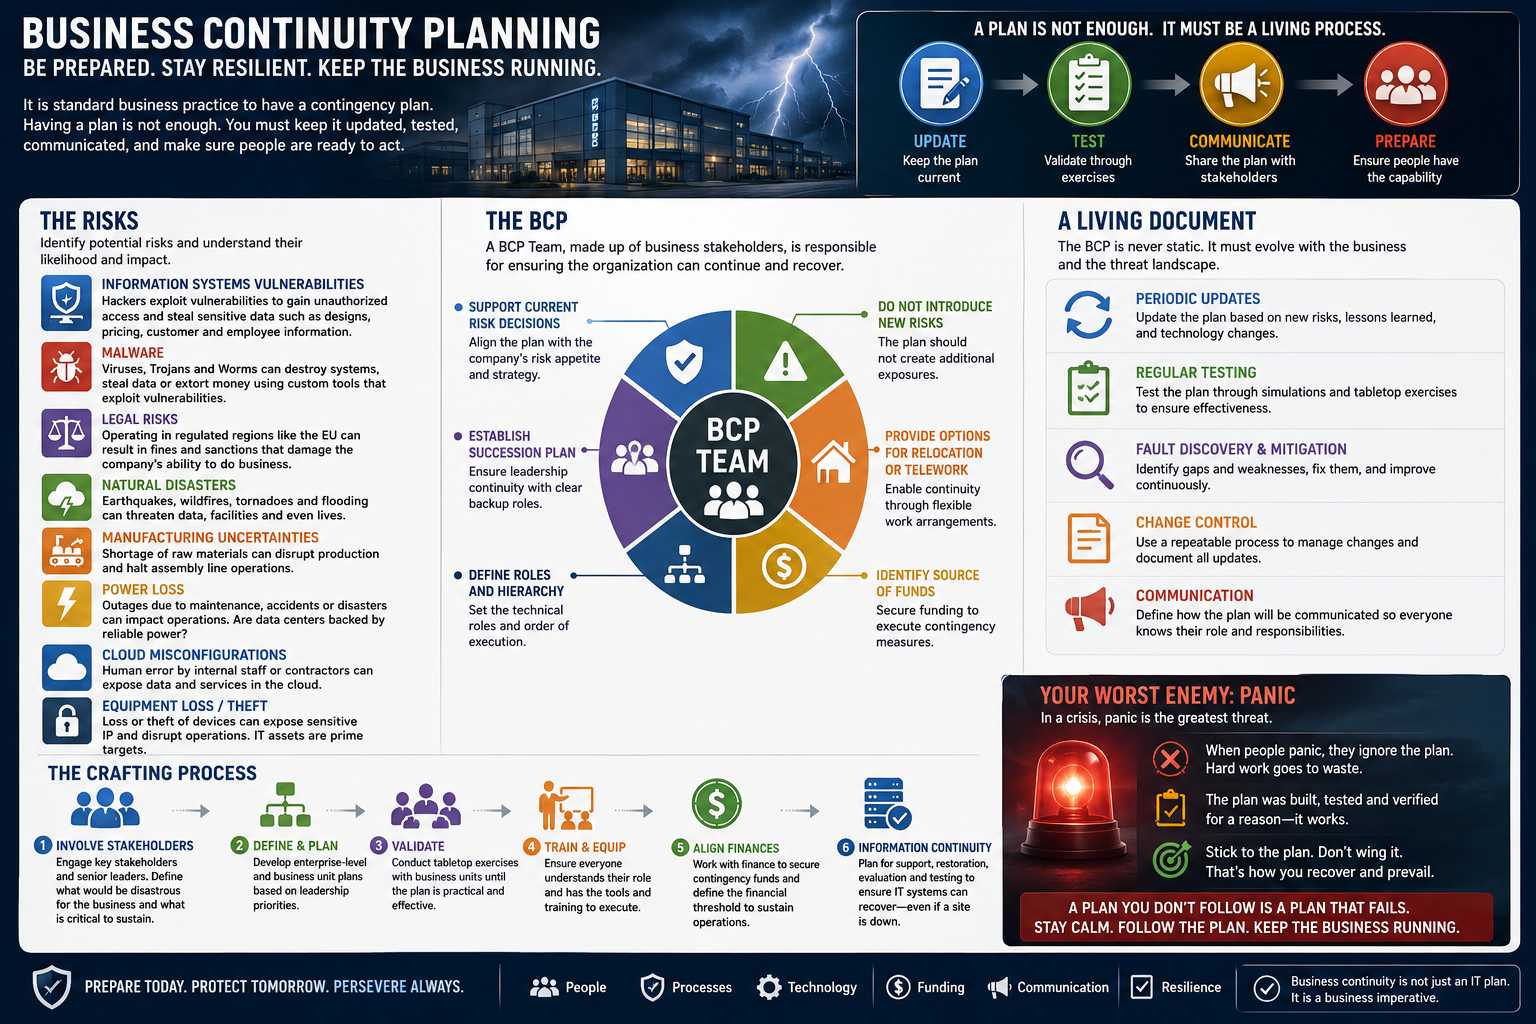
It is standard business practice for organizations to have a contingency plan after acknowledging the various threats and risks that it faces. Having a plan in place, however, is not enough. The organization must periodically update the plan, test how well it works, communicate it to stakeholders, and ensure that people have the capability to…
-
Information Security Requirements For U.S. Federal Contractors
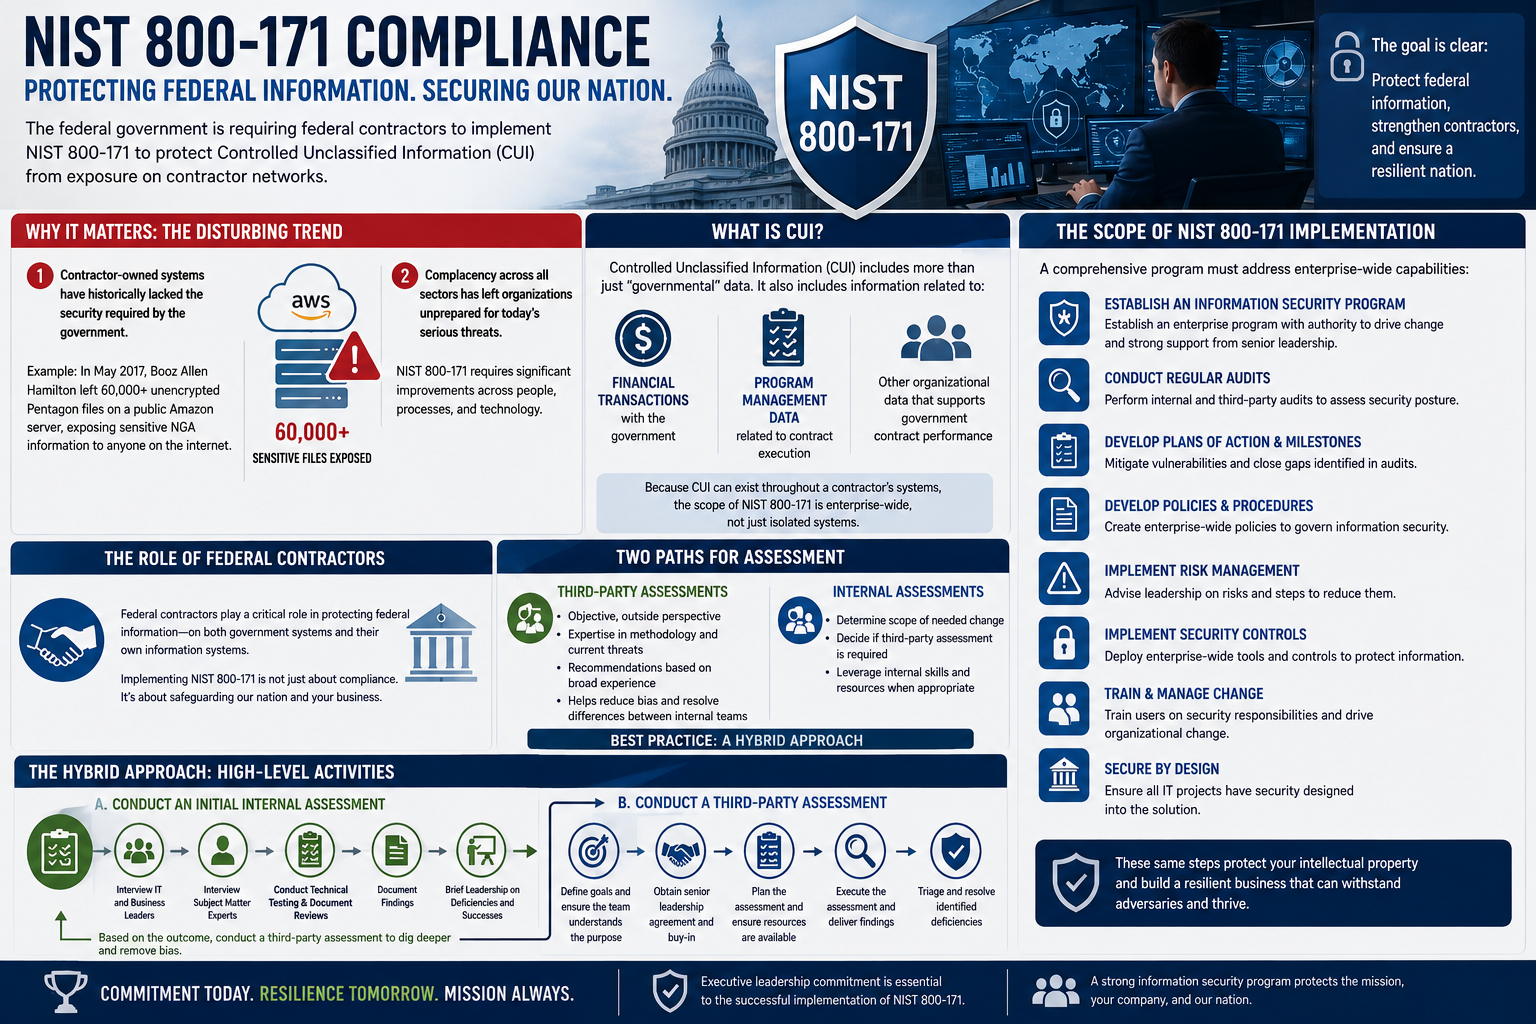
The federal government is requiring federal contractors to implement specific guidance in the form of NIST 800-171 in an effort to curb the trend of federal government data being exposed on contractor networks. This disturbing trend has occurred for a few reasons. First, federal contracts often require the use of contractor-owned information systems to process federal information. These…
-
The Attacks of the Future
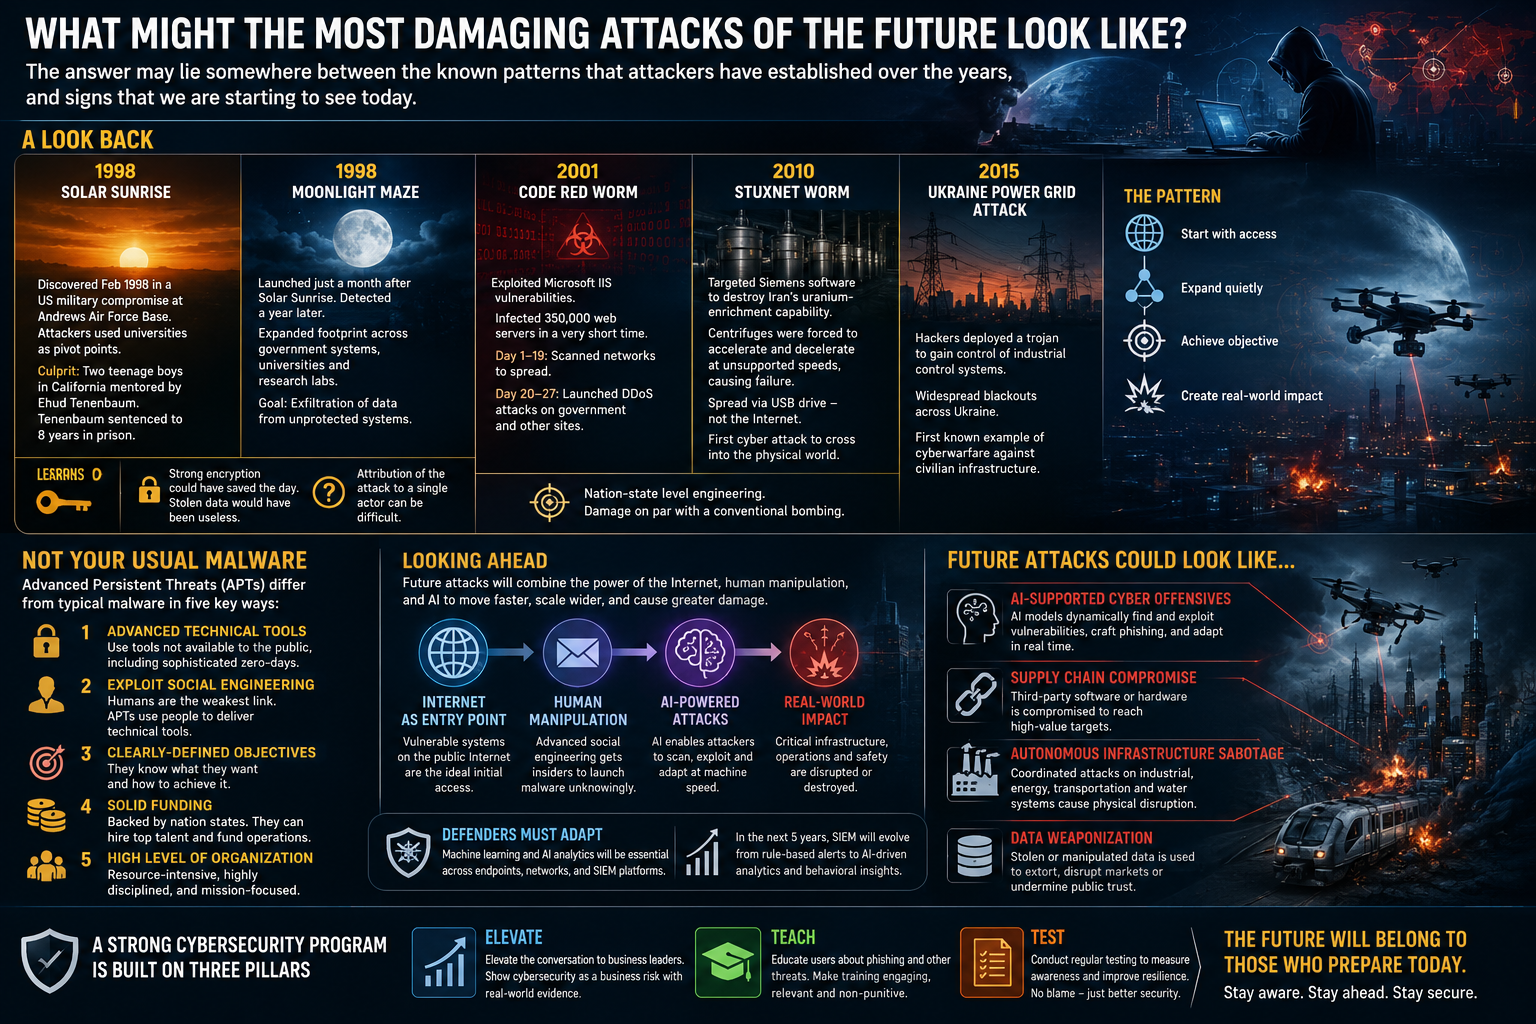
What might the most damaging attacks of the future look like? The answer to the question may lie somewhere between the known patterns that attackers have established over the years, and signs that we are starting to see today. A look back It started with the sun and the moon. Solar Sunrise was discovered in…
-

Information Security Handbook
View Information Security Handbook on Amazon I wrote Information Security Handbook as a practical guide to building and operating an information security program that fits the organization it is intended to protect. The book starts with the fundamentals of information security, then moves into threat modeling, risk management, security planning, continuous testing and monitoring, incident…
-
Drones, AI, and Security – The Future of Terrorism and Warfare
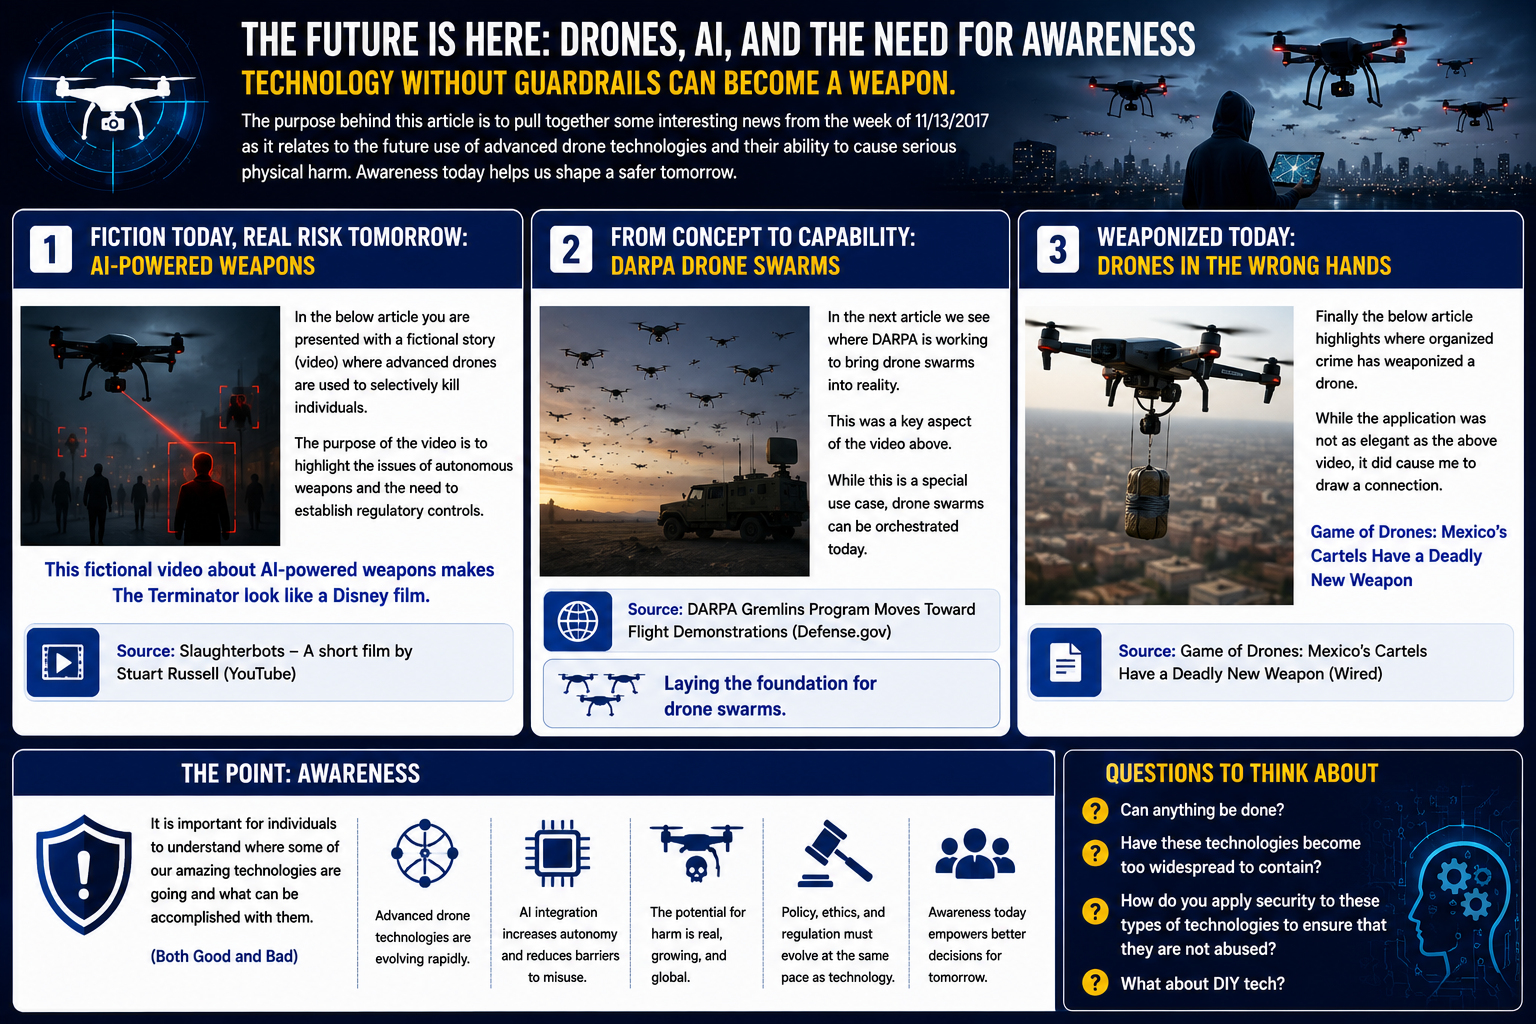
The purpose behind this article is to pull together some interesting news from the week of 11/13/2017 as it relates to the future use of advanced drone technologies and their ability to cause serious physical harm. In the below article you are presented with a fictional story (video) where advanced drones are used to selectively…